
Oracle Critical Patch Update January 2012
Released January 2012 · Oracle's advisory ↗ · ← Java SE Critical Patch Update, October 2011 · Java SE Critical Patch Update, February 2012 →
78 CVEs in this release, one square each
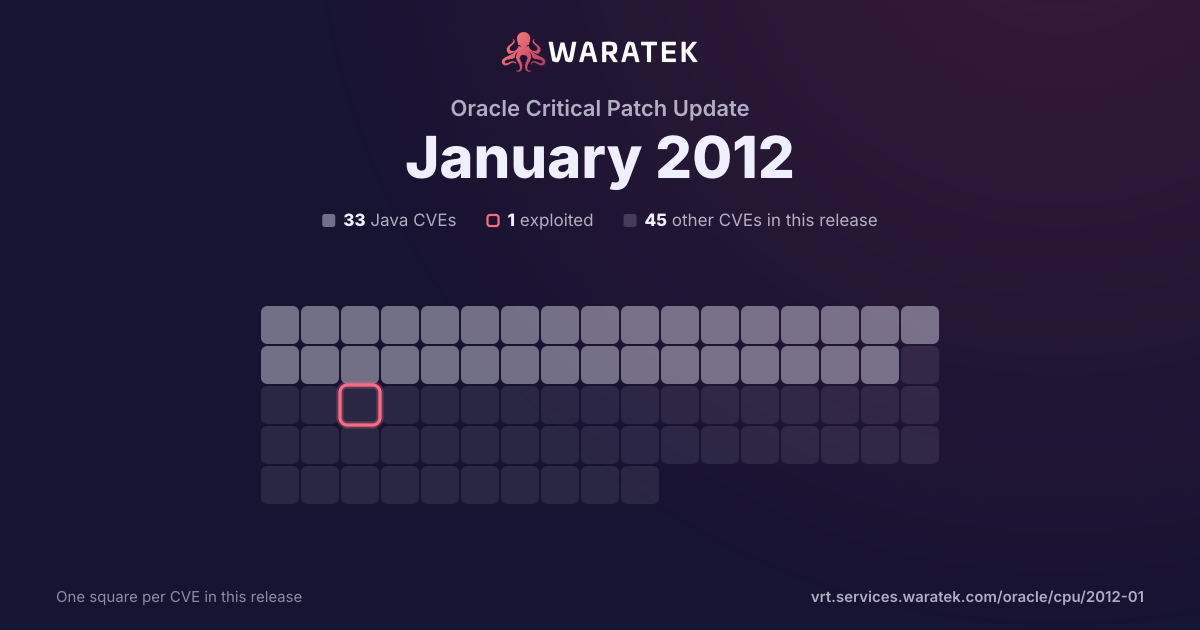
By status
No exploit published. For 33 of them, Oracle's security advisory is the source of public detail.
Overview 4 matches · 0 in Waratek scope · 0 protected · 1 exploited · 0 CISA KEV · 2 public PoC · 2 EPSS ≥ 0.5
4matches
0in Waratek scope0.0%
0protected0.0%
1exploited25.0%
0CISA KEV0.0%
2public PoC50.0%
2EPSS ≥ 0.550.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
1
25.0%
Not applicable
3
75.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
4
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
25.0%
Working exploit published
1
25.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
2
50.0%
split by
peak 3 / month
Aug 11Sep 11Oct 11Nov 11Dec 11
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2011-5035 | Medium | 2011-12-30 | Outside Waratek scope | Working exploit published | Oracle Glassfish 2.1.1, 3.0.1, and 3.1.1, as used in Communications Server 2.0, Sun Java System Application Server 8.1 and 8.2, and possibly other products, computes hash values for form parameters without restricting the ability to trigger hash collisions predictably, which allows remote attackers to cause a denial of service (CPU consumption) by sending many crafted parameters, aka Oracle security ticket S0104869. |
| CVE-2011-4517 | Medium | 2011-12-15 | Not applicable | No public exploit | The jpc_crg_getparms function in libjasper/jpc/jpc_cs.c in JasPer 1.900.1 uses an incorrect data type during a certain size calculation, which allows remote attackers to trigger a heap-based buffer overflow and execute arbitrary code, or cause a denial of service (heap memory corruption), via a crafted component registration (CRG) marker segment in a JPEG2000 file. |
| CVE-2011-4516 | Medium | 2011-12-15 | Not applicable | No public exploit | Heap-based buffer overflow in the jpc_cox_getcompparms function in libjasper/jpc/jpc_cs.c in JasPer 1.900.1 allows remote attackers to execute arbitrary code or cause a denial of service (memory corruption) via a crafted numrlvls value in a coding style default (COD) marker segment in a JPEG2000 file. |
| CVE-2011-3192 | High | 2011-08-29 | Not applicable | Exploited | The byterange filter in the Apache HTTP Server 1.3.x, 2.0.x through 2.0.64, and 2.2.x through 2.2.19 allows remote attackers to cause a denial of service (memory and CPU consumption) via a Range header that expresses multiple overlapping ranges, as exploited in the wild in August 2011, a different vulnerability than CVE-2007-0086. |