
Oracle Critical Patch Update January 2012
Released January 2012 · Oracle's advisory ↗ · ← Java SE Critical Patch Update, October 2011 · Java SE Critical Patch Update, February 2012 →
78 CVEs in this release, one square each
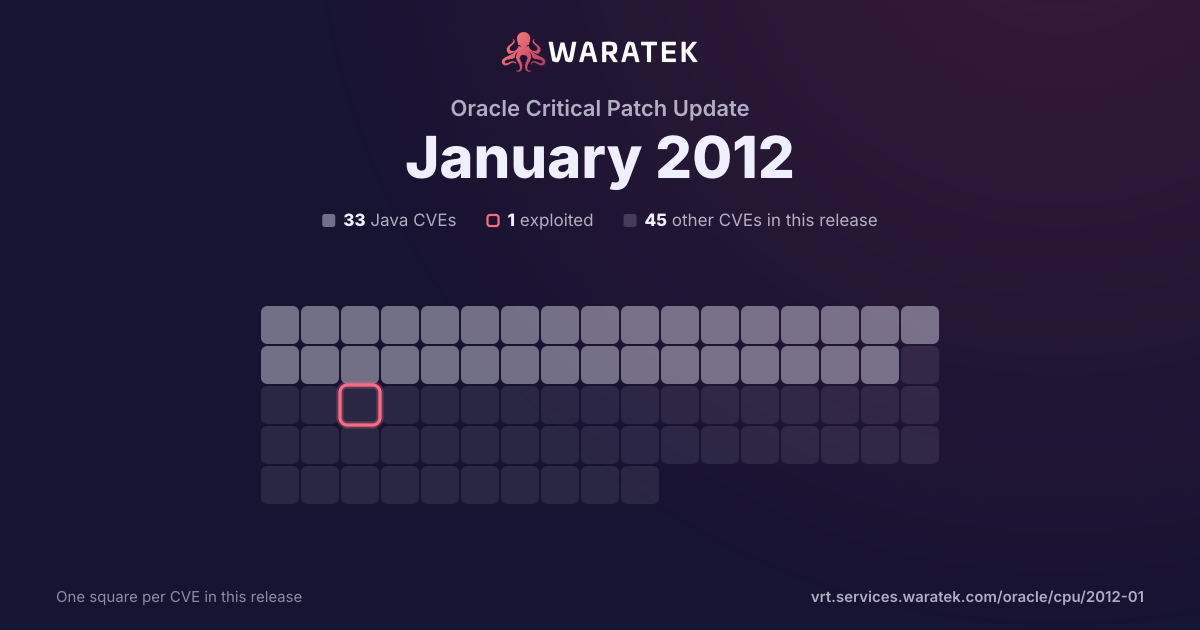
By status
1Mitigation candidate33No exploit published2Outside Waratek scope42Not applicable
1Exploited, marked by the ring
No exploit published. For 33 of them, Oracle's security advisory is the source of public detail.
Overview 4 matches · 0 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 1 EPSS ≥ 0.5
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
1
25.0%
No exploit published
3
75.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
4
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
25.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
3
75.0%
split by
peak 3 / month
Dec 11Jan 12
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2012-0104 | Medium | 2012-01-18 | No exploit published | No public exploit | Unspecified vulnerability in Oracle GlassFish Enterprise Server 3.0.1 and 3.1.1 allows remote attackers to affect availability via unknown vectors related to Web Container. |
| CVE-2011-3573 | Medium | 2012-01-18 | No exploit published | No public exploit | Unspecified vulnerability in Oracle Communications Unified 7.0 allows remote authenticated users to affect availability via unknown vectors related to Calendar Server. |
| CVE-2011-3565 | Medium | 2012-01-18 | No exploit published | No public exploit | Unspecified vulnerability in Oracle Communications Unified 7.0 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Calendar Server. |
| CVE-2011-5035 | Medium | 2011-12-30 | Mitigation candidate | Working exploit published | Oracle Glassfish 2.1.1, 3.0.1, and 3.1.1, as used in Communications Server 2.0, Sun Java System Application Server 8.1 and 8.2, and possibly other products, computes hash values for form parameters without restricting the ability to trigger hash collisions predictably, which allows remote attackers to cause a denial of service (CPU consumption) by sending many crafted parameters, aka Oracle security ticket S0104869. |