
Oracle Critical Patch Update October 2011
Released October 2011 · Oracle's advisory ↗ · ← Critical Patch Update, July 2011 · Java SE Critical Patch Update, October 2011 →
57 CVEs in this release, one square each
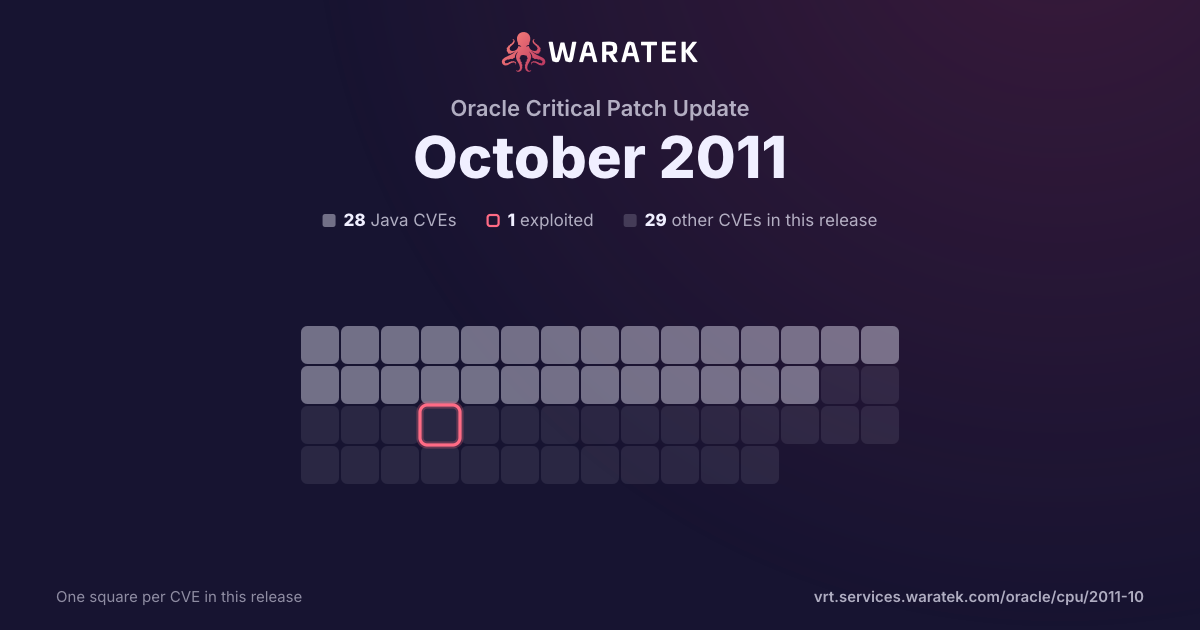
By status
No exploit published. For 28 of them, Oracle's security advisory is the source of public detail.
Overview 18 matches · 7 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
18matches
7in Waratek scope38.9%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
7
38.9%
Outside Waratek scope
2
11.1%
Not applicable
9
50.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
18
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
18
100.0%
split by
peak 18 / month
Oct 11
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2011-3541 | Low | 2011-10-18 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.3.5 and 8.3.7 allows local users to affect availability via unknown vectors related to Outside In Filters. |
| CVE-2011-3539 | Low | 2011-10-18 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and 11 Express allows local users to affect availability via unknown vectors related to Zones. |
| CVE-2011-3536 | Low | 2011-10-18 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 allows local users to affect availability, related to DTrace Software Library (libdtrace). |
| CVE-2011-3523 | Low | 2011-10-18 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Web Services Manager component in Oracle Fusion Middleware 10.1.3.5.0 and 10.1.3.5.1 allows remote authenticated users to affect integrity, related to WSM Console, a different vulnerability than CVE-2011-2237. |
| CVE-2011-3522 | Low | 2011-10-18 | Not applicable | No public exploit | Unspecified vulnerability in SysFW 8.0 on certain SPARC T3, Netra SPARC T3, Sun Fire, and Sun Blade based servers allows local users to affect confidentiality, related to Integrated Lights Out Manager CLI. |
| CVE-2011-3520 | Low | 2011-10-18 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.49, 8.50, and 8.51 allows remote authenticated users to affect integrity via unknown vectors related to Personalization. |
| CVE-2011-3519 | Low | 2011-10-18 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Framework component in Oracle E-Business Suite 12.1.2 and 12.1.3 allows remote authenticated users to affect confidentiality, related to REST Services. |
| CVE-2011-3511 | Low | 2011-10-18 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Database Vault component in Oracle Database Server 10.2.0.3, 10.2.0.4, 10.2.0.5, 11.1.0.7, and 11.2.0.2 allows remote authenticated users to affect integrity and availability via unknown vectors related to Privileged Account. |
| CVE-2011-3507 | Low | 2011-10-18 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Communications Unified component in Oracle Sun Products Suite 7.0 allows remote authenticated users to affect integrity via unknown vectors related to Messaging Server. |
| CVE-2011-2327 | Low | 2011-10-18 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Communications Unified component in Oracle Sun Products Suite 7.0 allows local users to affect confidentiality via unknown vectors related to Delegated Administrator. |
| CVE-2011-2322 | Low | 2011-10-18 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Database Vault component in Oracle Database Server 11.1.0.7 allows remote authenticated users to affect integrity and availability, related to SYSDBA. |
| CVE-2011-2318 | Low | 2011-10-18 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 9.2.4.0, 10.0.2.0, 10.3.3.0, 10.3.4.0, and 10.3.5.0 allows local users to affect confidentiality, related to WLS Security. |
| CVE-2011-2312 | Low | 2011-10-18 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 allows local users to affect confidentiality, related to ZFS. |
| CVE-2011-2311 | Low | 2011-10-18 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 allows local users to affect availability, related to ZFS, a different vulnerability than CVE-2011-2313. |
| CVE-2011-2303 | Low | 2011-10-18 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Application Object Library component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.2, and 12.1.3 allows remote authenticated users to affect integrity via unknown vectors related to Attachments / File Upload. |
| CVE-2011-2292 | Low | 2011-10-18 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 9 and 11 Express allows local users to affect confidentiality and integrity via unknown vectors related to xscreensaver. |
| CVE-2011-2286 | Low | 2011-10-18 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and 11 Express allows remote authenticated users to affect availability, related to ZFS. |
| CVE-2011-2237 | Low | 2011-10-18 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Web Services Manager component in Oracle Fusion Middleware 10.1.3.5.0 and 10.1.3.5.1 allows remote authenticated users to affect integrity, related to WSM Console, a different vulnerability than CVE-2011-3523. |