
Oracle Critical Patch Update July 2011
Released July 2011 · Oracle's advisory ↗ · ← Java SE Critical Patch Update, June 2011 · Critical Patch Update, October 2011 →
78 CVEs in this release, one square each
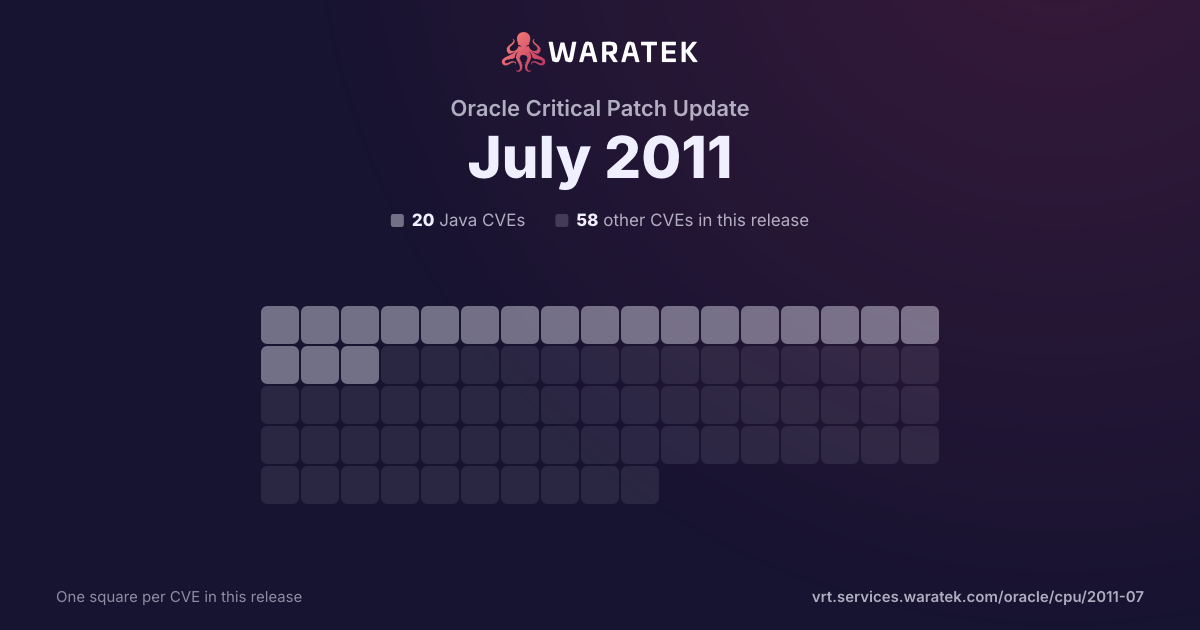
By status
No exploit published. For 20 of them, Oracle's security advisory is the source of public detail.
Overview 32 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
32matches
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
32
100.0%
Not applicable
0
0.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
32
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
32
100.0%
split by
peak 31 / month
May 10Jul 10Sep 10Nov 10Jan 11Mar 11May 11Jul 11
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2011-2264 | Medium | 2011-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.3.2.0 and 8.3.5.0 allows context-dependent attackers to affect confidentiality, integrity, and availability via unknown vectors related to Outside In Filters. NOTE: the previous information was obtained from the July 2011 CPU. Oracle has not commented on claims from a reliable third party that this is a stack-based buffer overflow in the imcdr2.flt library for the CorelDRAW parser. |
| CVE-2011-2257 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Database Target Type Menus component in Oracle Database Server 10.1.0.5, 10.2.0.3, 10.2.0.4, 10.2.0.5, 11.1.0.7, 11.2.0.1, and 11.2.0.2; and Oracle Enterprise Manager Grid Control 10.1.0.6, 10.2.0.5, and 11.1.0.1; allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2011-2253 | High | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 10.2.0.3, 10.2.0.4, 10.2.0.5, 11.1.0.7, 11.2.0.1, and 11.2.0.2 allows remote authenticated users to affect confidentiality, integrity, and availability, related to SYSDBA. |
| CVE-2011-2248 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the SQL Performance Advisories/UIs component in Oracle Database Server 11.1.0.7, 11.2.0.1, and 11.2.0.2; and Oracle Enterprise Manager Grid Control 10.1.0.6, 10.2.0.5, and 11.1.0.1; allows remote attackers to affect confidentiality, integrity, and availability, related to SQL Details UI & Explain Plan. |
| CVE-2011-2244 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Security Framework component in Oracle Database Server 10.1.0.5, 10.2.0.3, 10.2.0.4, 10.2.0.5, 11.1.0.7, 11.2.0.1, and 11.2.0.2; and Enterprise Manager Grid Control 10.1.0.6, 10.2.0.5, and 11.1.0.1; allows remote attackers to affect confidentiality and integrity via unknown vectors related to Authentication. |
| CVE-2011-2243 | Low | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 11.1.0.7.3, 11.2.0.1, and 11.2.0.2 allows remote authenticated users to affect integrity, related to SYSDBA. |
| CVE-2011-2242 | Low | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 11.2.0.1 and 11.2.0.2 allows local users to affect confidentiality, related to XML DB FTP. |
| CVE-2011-2240 | Low | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Oracle Universal Installer component in Oracle Database Server 10.1.0.5 allows local users to affect confidentiality via unknown vectors. |
| CVE-2011-2239 | High | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 10.2.0.3, 10.2.0.4, 10.2.0.5, 11.1.0.7, 11.2.0.1, and 11.2.0.2 allows remote authenticated users to affect confidentiality, integrity, and availability, related to XMLSEQ_IMP_T. |
| CVE-2011-2238 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Database Vault component in Oracle Database Server 10.2.0.3, 10.2.0.4, 10.2.0.5, 11.1.0.7, and 11.2.0.1 allows remote authenticated users to affect integrity, related to DBMS_SYS_SQL. |
| CVE-2011-2232 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the XML Developer Kit component in Oracle Database Server 10.1.0.5, 10.2.0.3, 10.2.0.4, 11.1.0.7, and 11.2.0.1, and Oracle Fusion Middleware 10.1.3.5, allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2011-2231 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the XML Developer Kit component in Oracle Database Server 10.1.0.5, 10.2.0.3, 10.2.0.4, 10.2.0.5, 11.1.0.7, and 11.2.0.1, Oracle Fusion Middleware 10.1.3.5, allows remote attackers to affect availability via unknown vectors. |
| CVE-2011-2230 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 10.1.0.5, 10.2.0.3, 10.2.0.4, 10.2.0.5, 11.1.0.7, and 11.2.0.1 allows remote attackers to affect availability via unknown vectors. |
| CVE-2011-0882 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Content Management component in Oracle Database Server 10.1.0.5, 10.2.0.3, 10.2.0.4, and 11.1.0.7; and Oracle Enterprise Manager Grid Control 10.1.0.6, 10.2.0.5, and 11.1.0.1; allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Scheduler. |
| CVE-2011-0881 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the EMCTL component in Oracle Database Server 10.2.0.3, 10.2.0.4, and 11.1.0.7, and Oracle Enterprise Manager Grid Control 10.1.0.6, allows remote attackers to affect integrity via unknown vectors. |
| CVE-2011-0880 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 11.1.0.7, 11.2.0.1, and 11.2.0.2 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2011-0832 and CVE-2011-0835. |
| CVE-2011-0879 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Instance Management component in Oracle Database Server 10.1.0.5, 10.2.0.3, 10.2.0.4, 10.2.0.5, 11.1.0.7, 11.2.0.1, and 11.2.0.2; and Oracle Enterprise Manager Grid Control 10.1.0.6 and 10.2.0.5; allows remote attackers to affect integrity via unknown vectors. |
| CVE-2011-0877 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Instance Management component in Oracle Database Server 10.1.0.5, 10.2.0.3, and 10.2.0.4, and Oracle Enterprise Manager Grid Control 10.1.0.6, allows remote attackers to affect integrity via unknown vectors. |
| CVE-2011-0876 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Enterprise Manager Console component in Oracle Database Server 10.1.0.5, 10.2.0.3, 10.2.0.4, 10.2.0.5, 11.1.0.7, 11.2.0.1, and 11.2.0.2; and Oracle Enterprise Manager Grid Control 10.1.0.6 and 10.2.0.5; allows remote attackers to affect integrity via unknown vectors related to Security. |
| CVE-2011-0875 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the EMCTL component in Oracle Database Server 11.1.0.7 and Oracle Enterprise Manager Grid Control 10.1.0.6, 10.2.0.5, and 11.1.0.1 allows remote authenticated users to affect confidentiality and integrity via unknown vectors. |
| CVE-2011-0870 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Schema Management component in Oracle Database Server 10.1.0.5, 10.2.0.3, 10.2.0.4, 10.2.0.5, 11.1.0.7, 11.2.0.1, and 11.2.0.2; and Oracle Enterprise Manager Grid Control 10.1.0.6 and 10.2.0.5; allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2011-0852 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Security Management component in Oracle Database Server 10.1.0.5, 10.2.0.3, and 10.2.0.4; and Oracle Enterprise Manager Grid Control 10.1.0.6; allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Audit Administration. |
| CVE-2011-0848 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Security Framework component in Oracle Database Server 10.1.0.5, 10.2.0.3, 10.2.0.4, 10.2.0.5, 11.1.0.7, 11.2.0.1, and 11.2.0.2; and Oracle Enterprise Manager Grid Control 10.1.0.6 and 10.2.0.5; allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to User Model. |
| CVE-2011-0838 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 11.1.0.7, 11.2.0.1, and 11.2.0.2 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors related to create procedure privileges. |
| CVE-2011-0835 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 11.1.0.7, 11.2.0.1, and 11.2.0.2 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2011-0832 and CVE-2011-0880. |
| CVE-2011-0832 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 11.1.0.7, 11.2.0.1, and 11.2.0.2 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2011-0835 and CVE-2011-0880. |
| CVE-2011-0831 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Enterprise Config Management component in Oracle Database Server 10.1.0.5, 10.2.0.3, 10.2.0.4, 10.2.0.5, 11.1.0.7, 11.2.0.1, and 11.2.0.2; and Oracle Enterprise Manager Grid Control 10.1.0.6 and 10.2.0.5; allows remote authenticated users to affect confidentiality and integrity via unknown vectors. |
| CVE-2011-0830 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Event Management component in Oracle Database Server 10.1.0.5, 10.2.0.3, and 10.2.0.4, and Oracle Enterprise Manager Grid Control 10.1.0.6, allows remote attackers to affect integrity via unknown vectors related to Rules Management UI. |
| CVE-2011-0822 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Streams, AQ & Replication Mgmt component in Oracle Database Server 10.1.0.5 and 10.2.0.3, and Oracle Enterprise Manager Grid Control 10.1.0.6, allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2011-0816 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the CMDB Metadata & Instance APIs component in Oracle Database Server 10.1.0.5, 10.2.0.3, 10.2.0.4, 10.2.0.5, 11.1.0.7, 11.2.0.1, and 11.2.0.2; and Oracle Enterprise Manager Grid Control 10.1.0.6 and 10.2.0.5; allows remote authenticated users to affect confidentiality and integrity via unknown vectors. |
| CVE-2011-0811 | Medium | 2011-07-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Enterprise Config Management component in Oracle Database Server 10.1.0.5, 10.2.0.3, and 10.2.0.4, and Oracle Enterprise Manager Grid Control 10.1.0.6 and 10.2.0.5, allows local users to affect confidentiality via unknown vectors. |
| CVE-2010-1321 | Medium | 2010-05-19 | Outside Waratek scope | No public exploit | The kg_accept_krb5 function in krb5/accept_sec_context.c in the GSS-API library in MIT Kerberos 5 (aka krb5) through 1.7.1 and 1.8 before 1.8.2, as used in kadmind and other applications, does not properly check for invalid GSS-API tokens, which allows remote authenticated users to cause a denial of service (NULL pointer dereference and daemon crash) via an AP-REQ message in which the authenticator's checksum field is missing. |