
Oracle Critical Patch Update April 2011
Released April 2011 · Oracle's advisory ↗ · ← Java SE Critical Patch Update, February 2011 · Java SE Critical Patch Update, June 2011 →
72 CVEs in this release, one square each
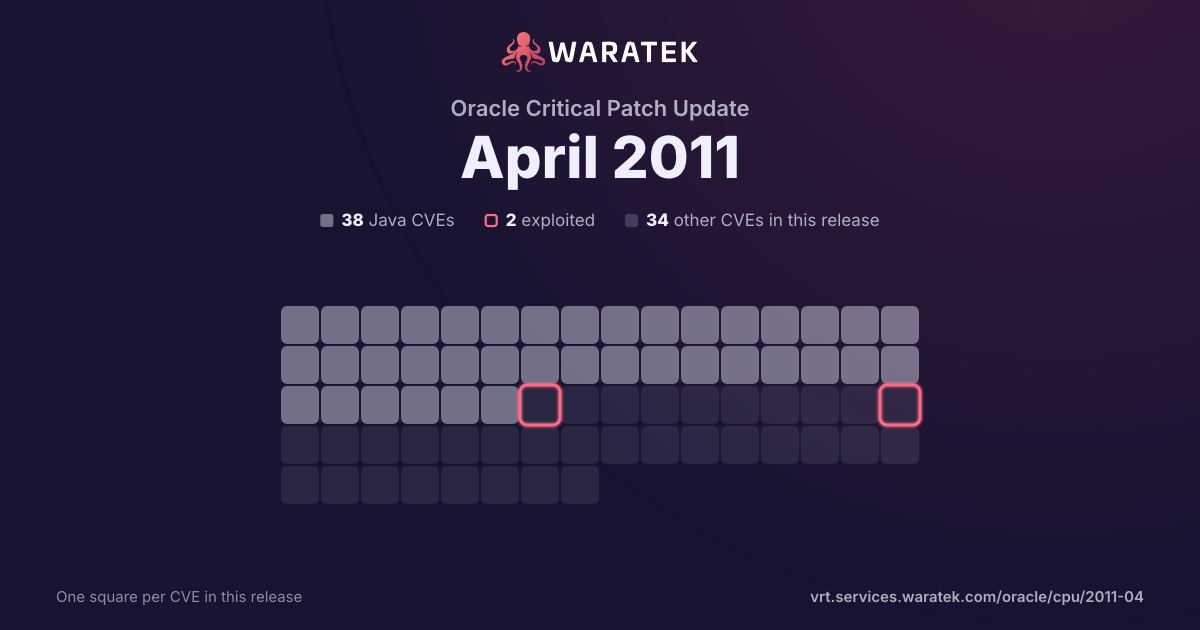
By status
3Mitigation candidate35No exploit published9Outside Waratek scope25Not applicable
2Exploited, marked by the ring
No exploit published. For 35 of them, Oracle's security advisory is the source of public detail.
Overview 3 matches · 1 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 0 EPSS ≥ 0.5
3matches
1in Waratek scope33.3%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
1public PoC33.3%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
1
33.3%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
2
66.7%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
3
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
33.3%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
2
66.7%
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2011-0411 | Medium | 2011-03-16 | Not applicable | No public exploit | The STARTTLS implementation in Postfix 2.4.x before 2.4.16, 2.5.x before 2.5.12, 2.6.x before 2.6.9, and 2.7.x before 2.7.3 does not properly restrict I/O buffering, which allows man-in-the-middle attackers to insert commands into encrypted SMTP sessions by sending a cleartext command that is processed after TLS is in place, related to a "plaintext command injection" attack. |
| CVE-2010-4476 | Medium | 2011-02-17 | Mitigation candidate | Working exploit published | The Double.parseDouble method in Java Runtime Environment (JRE) in Oracle Java SE and Java for Business 6 Update 23 and earlier, 5.0 Update 27 and earlier, and 1.4.2_29 and earlier, as used in OpenJDK, Apache, JBossweb, and other products, allows remote attackers to cause a denial of service via a crafted string that triggers an infinite loop of estimations during conversion to a double-precision binary floating-point number, as demonstrated using 2.2250738585072012e-308. |
| CVE-2010-3689 | Medium | 2011-01-28 | Not applicable | No public exploit | soffice in OpenOffice.org (OOo) 3.x before 3.3 places a zero-length directory name in the LD_LIBRARY_PATH, which allows local users to gain privileges via a Trojan horse shared library in the current working directory. |