
Oracle Critical Patch Update April 2011
Released April 2011 · Oracle's advisory ↗ · ← Java SE Critical Patch Update, February 2011 · Java SE Critical Patch Update, June 2011 →
72 CVEs in this release, one square each
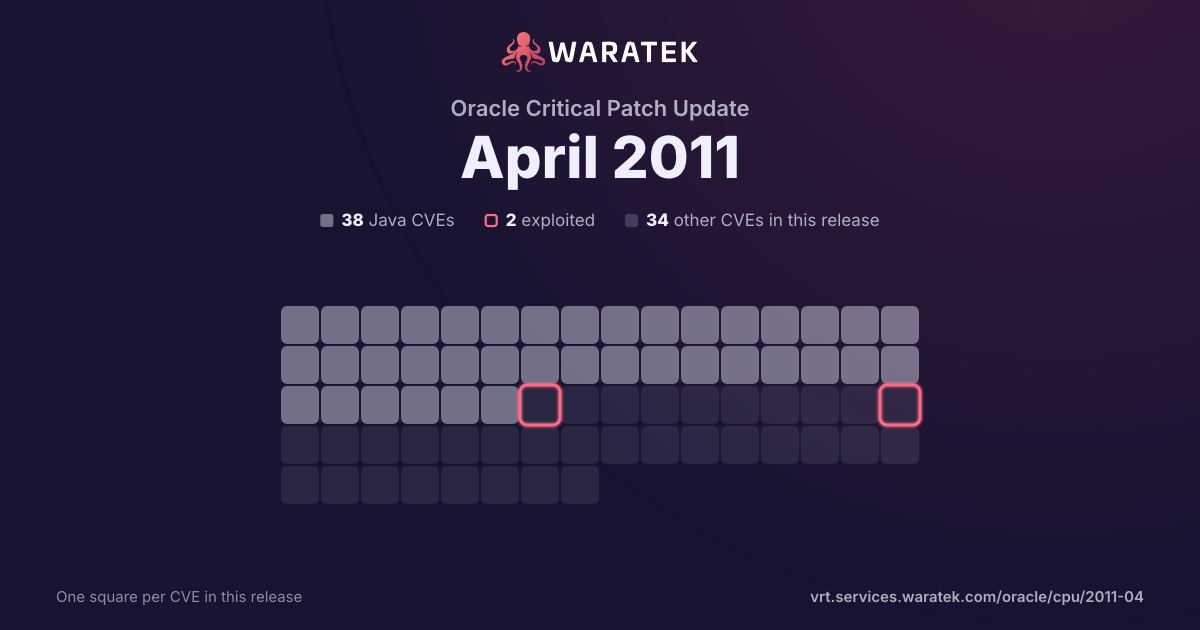
By status
3Mitigation candidate35No exploit published9Outside Waratek scope25Not applicable
2Exploited, marked by the ring
No exploit published. For 35 of them, Oracle's security advisory is the source of public detail.
Overview 67 matches · 35 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
67matches
35in Waratek scope52.2%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
35
52.2%
Outside Waratek scope
8
11.9%
Not applicable
24
35.8%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
67
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
67
100.0%
split by
peak 58 / month
Jan 11Feb 11Mar 11Apr 11
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2011-0861 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in Oracle PeopleSoft Enterprise HRMS 9.0 Update 2011-B and 9.1 Update 2011-B allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Global Payroll Core. |
| CVE-2011-0860 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in Oracle PeopleSoft Enterprise HRMS 9.0 Update 2011-B and 9.1 Update 2011-B allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Global Payroll - Spain. |
| CVE-2011-0859 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in Oracle PeopleSoft Enterprise HRMS 9.0 Tax Update 11-B and 9.1 Tax Update 11-B allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Global Payroll - North America. |
| CVE-2011-0858 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in Oracle PeopleSoft Enterprise HRMS 9.0 Bundle #15 and 9.1 Bundle #5 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Talent Acquisition Manager. |
| CVE-2011-0857 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in Oracle PeopleSoft Enterprise HRMS 9.0 Bundle #15 and 9.1 Bundle #5 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Pension Administration. |
| CVE-2011-0856 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in Oracle PeopleSoft Enterprise 8.49 GA through 8.49.30, 8.50 GA through 8.50.17, and 8.51 GA through 8.51.07 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2011-0855 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in the InForm component in Oracle Industry Applications 4.5, 4.6, and 5.0 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Core. |
| CVE-2011-0854 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in Oracle PeopleSoft Enterprise HRMS 9.1 Bundle #5 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to ePerformance. |
| CVE-2011-0853 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in Oracle PeopleSoft Enterprise HRMS 9.0 Bundle #15 and 9.1 Bundle #5 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to ePerformance. |
| CVE-2011-0851 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in Oracle PeopleSoft Enterprise ELS 9.0 Bundle #19 and 9.1 Bundle #5 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Enterprise Learning Mgmt. |
| CVE-2011-0850 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in Oracle PeopleSoft Enterprise CRM 8.9 Bundle #41 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Order Capture. |
| CVE-2011-0849 | Medium | 2011-04-20 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Java Dynamic Management Kit 5.1 allows remote attackers to affect integrity, related to HTML Adaptor. |
| CVE-2011-0847 | Medium | 2011-04-20 | Not applicable | No public exploit | Unspecified vulnerability in the OpenSSO Enterprise and Sun Java System Access Manager components in Oracle Sun Products Suite 7.1 and 8.0 allows remote authenticated users to affect confidentiality via unknown vectors related to Authentication. |
| CVE-2011-0846 | Medium | 2011-04-20 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Sun Java System Access Manager Policy Agent 2.2 allows remote attackers to affect availability via unknown vectors related to Web Proxy Agent. |
| CVE-2011-0844 | Medium | 2011-04-20 | Not applicable | No public exploit | Unspecified vulnerability in the OpenSSO Enterprise and Sun Java System Access Manager components in Oracle Sun Products Suite 7.1 and 8.0 allows remote attackers to affect integrity via unknown vectors related to Authentication. |
| CVE-2011-0843 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel CRM Core component in Oracle Siebel CRM 7.8.2, 8.0.0, and 8.1.1 allows remote attackers to affect integrity via unknown vectors related to Globalization - Automotive. |
| CVE-2011-0841 | High | 2011-04-20 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 11 Express allows remote attackers to affect availability, related to TCP/IP. |
| CVE-2011-0840 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in Oracle PeopleSoft Enterprise PeopleTools 8.49 GA through 8.49.30 allows remote authenticated users to affect confidentiality via unknown vectors related to File Processing. |
| CVE-2011-0839 | Low | 2011-04-20 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 9, 10, and 11 Express allows local users to affect availability, related to LOFS. |
| CVE-2011-0837 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in the Agile Technology Platform component in Oracle Supply Chain Products Suite 9.3.0.2 and 9.3.1 allows remote attackers to affect confidentiality via unknown vectors related to Security. |
| CVE-2011-0834 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel CRM Core component in Oracle Siebel CRM 8.0.0 and 8.1.1 allows remote attackers to affect integrity via unknown vectors related to Globalization - Automotive. |
| CVE-2011-0833 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel CRM Core component in Oracle Siebel CRM 7.8.2, 8.0.0, and 8.1.1 allows remote attackers to affect integrity, related to UIF Client. |
| CVE-2011-0829 | Medium | 2011-04-20 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and 11 Express allows local users to affect availability, related to Kernel/SPARC. |
| CVE-2011-0828 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in Oracle PeopleSoft Enterprise 8.8 Bundle #13 allows remote attackers to affect integrity via unknown vectors related to Application Portal. |
| CVE-2011-0827 | Low | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise component in Oracle PeopleSoft Products 8.50 GA through 8.50.17 and 8.51 GA through 8.51.07 allows remote authenticated users to affect integrity via unknown vectors related to PeopleTools. |
| CVE-2011-0826 | Low | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in Oracle PeopleSoft Enterprise 8.8 Bundle #13, 8.9 Bundle #7, 9.0 Bundle #7, and 9.1 Bundle #4 allows remote authenticated users to affect integrity via unknown vectors related to Application Portal. |
| CVE-2011-0825 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in Oracle JD Edwards EnterpriseOne Tools 8.9 GA through 8.98.4.1 and OneWorld Tools through 24.1.3 allows remote attackers to affect confidentiality, integrity, and availability, related to Enterprise Infrastructure SEC. |
| CVE-2011-0824 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in Oracle JD Edwards EnterpriseOne Tools 8.9 GA through 8.98.4.1 and OneWorld Tools through 24.1.3 allows remote attackers to affect confidentiality and integrity, related to Enterprise Infrastructure SEC. |
| CVE-2011-0823 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in Oracle JD Edwards EnterpriseOne Tools 8.9 GA through 8.98.4.1 and OneWorld Tools through 24.1.3 allows remote attackers to affect integrity, related to Enterprise Infrastructure SEC, a different vulnerability than CVE-2011-0819. |
| CVE-2011-0821 | Low | 2011-04-20 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 8, 9, and 10 allows local users to affect confidentiality and integrity via unknown vectors related to uucp. |
| CVE-2011-0820 | Medium | 2011-04-20 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10, and 11 Express allows remote attackers to affect availability via unknown vectors related to Kernel. |
| CVE-2011-0819 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in Oracle JD Edwards EnterpriseOne Tools 8.9 GA through 8.98.4.1 and OneWorld Tools through 24.1.3 allows remote attackers to affect integrity, related to Enterprise Infrastructure SEC, a different vulnerability than CVE-2011-0823. |
| CVE-2011-0818 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in Oracle JD Edwards EnterpriseOne Tools 8.9 GA through 8.98.4.1 and OneWorld Tools through 24.1.3 allows remote attackers to affect availability, related to Enterprise Infrastructure SEC. |
| CVE-2011-0813 | Medium | 2011-04-20 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 8, 9, 10, and 11 Express allows local users to affect availability via unknown vectors related to Kernel, a different vulnerability than CVE-2012-0098. |
| CVE-2011-0812 | Low | 2011-04-20 | Not applicable | No public exploit | Unspecified vulnerability in the Solaris component in Oracle Solaris 8, 9, 10, and 11 Express allows local users to affect availability via unknown vectors related to Kernel. |
| CVE-2011-0810 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability Oracle JD Edwards EnterpriseOne Tools 8.9 GA through 8.98.4.1 and OneWorld Tools through 24.1.3 allows remote attackers to affect availability, related to Enterprise Infrastructure SEC. |
| CVE-2011-0809 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in the Web ADI component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.1, 12.1.2, and 12.1.3 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2011-0808 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.3.2.0 and 8.3.5.0 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Outside In Filters. NOTE: the previous information was obtained from the April 2011 CPU. Oracle has not commented on claims from a reliable third party that this issue is in (a) vswk6.dll or (b) libvs_wk6.so in Outside In 8.1.0.4037 through 8.3.5.5684, involving the Lotus 123 parser. |
| CVE-2011-0806 | Medium | 2011-04-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Network Foundation component in Oracle Database Server 10.1.0.5, 10.2.0.4, 10.2.0.5, 11.1.0.7, 11.2.0.1, and 11.2.0.2, when running on Windows, allows remote attackers to affect availability via unknown vectors. |
| CVE-2011-0805 | Medium | 2011-04-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the UIX component in Oracle Database Server 10.1.0.5, 10.2.0.4, 11.1.0.7, and 11.2.0.1 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2011-0804 | Low | 2011-04-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Database Vault component in Oracle Database Server 10.2.0.3, 10.2.0.4, 10.2.0.5, 11.1.0.7, 11.2.0.1, and 11.2.0.2 allows remote authenticated users to affect confidentiality and integrity via unknown vectors. |
| CVE-2011-0803 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in the JD Edwards EnterpriseOne Tools component in Oracle JD Edwards Products 8.9 GA through 8.98.4.1, and OneWorld Tools through 24.1.3, allows remote attackers to affect integrity and availability, related to Enterprise Infrastructure SEC. |
| CVE-2011-0801 | Low | 2011-04-20 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and 11 Express allows local users to affect confidentiality and integrity via unknown vectors related to cp. |
| CVE-2011-0800 | Medium | 2011-04-20 | Not applicable | No public exploit | Unspecified vulnerability in the Solaris component in Oracle Solaris 8, 9, 10, and 11 Express allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Administration Utilities. |
| CVE-2011-0799 | Medium | 2011-04-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Oracle Warehouse Builder component in Oracle Database Server 10.2.0.5 (OWB), 11.1.0.7, and 11.2.0.1 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors related to Oracle Warehouse Builder User Account. |
| CVE-2011-0798 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in the Portal component in Oracle Fusion Middleware 10.1.2.3 and 11.1.1.2.0 allows remote attackers to affect integrity via unknown vectors related to Midtier Infrastructure. |
| CVE-2011-0797 | Low | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in the Applications Install component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.1, 12.1.2, and 12.1.3 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2011-0796 | Low | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in the Applications Install component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.1, 12.1.2, and 12.1.3 allows local users to affect confidentiality via unknown vectors. |
| CVE-2011-0795 | Low | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in the Single Sign On component in Oracle Fusion Middleware 10.1.2.3 allows remote authenticated users to affect integrity via unknown vectors related to Administration and Monitoring. |
| CVE-2011-0794 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.3.5.0 allows local users to affect confidentiality, integrity, and availability, related to File ID SDK. NOTE: the previous information was obtained from the April 2011 CPU. Oracle has not commented on claims from a reliable third party that this issue is in (a) sccut.dll or (b) libsc_ut.so in Outside In 8.3.5.x through 8.3.5.5684, as used when using the CAB file identification functionality to parse OneNote (.onepkg) files and other formats. |
| CVE-2011-0793 | Low | 2011-04-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Database Vault component in Oracle Database Server 10.2.0.3, 10.2.0.4, 10.2.0.5, 11.1.0.7, and 11.2.0.1 allows remote authenticated users to affect integrity and availability, related to SYSDBA. |
| CVE-2011-0792 | Medium | 2011-04-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Oracle Warehouse Builder component in Oracle Database Server 10.2.0.5 (OWB) and 11.1.0.7 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors related to Dimensional Data Modeling. |
| CVE-2011-0791 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in the Application Object Library component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.1, 12.1.2, and 12.1.3 allows remote attackers to affect confidentiality via unknown vectors related to Data Export. |
| CVE-2011-0790 | Low | 2011-04-20 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 9 and 10 allows local users to affect confidentiality via unknown vectors related to wbem. |
| CVE-2011-0789 | Medium | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle HTTP Server component in Oracle Fusion Middleware 10.1.2.3 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2011-0787 | Medium | 2011-04-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Application Service Level Management component in Oracle Database Server 11.1.0.7 and Enterprise Manager Grid Control allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Service Level Agreements. |
| CVE-2011-0785 | Medium | 2011-04-20 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Oracle Help component in Oracle Database Server 11.1.0.7, 11.2.0.1, 11.2.0.2, 10.1.0.5, 10.2.0.3, 10.2.0.4, 10.2.0.5, and 10.1.0.5; and Oracle Fusion Middleware 11.1.1.2.0, 11.1.1.3.0, and 11.1.1.4.0 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2011-0412 | Low | 2011-04-19 | Not applicable | No public exploit | Oracle Solaris 8, 9, and 10 stores back-out patch files (undo.Z) unencrypted with world-readable permissions under /var/sadm/pkg/, which allows local users to obtain password hashes and conduct brute force password guessing attacks. |
| CVE-2011-0411 | Medium | 2011-03-16 | Not applicable | No public exploit | The STARTTLS implementation in Postfix 2.4.x before 2.4.16, 2.5.x before 2.5.12, 2.6.x before 2.6.9, and 2.7.x before 2.7.3 does not properly restrict I/O buffering, which allows man-in-the-middle attackers to insert commands into encrypted SMTP sessions by sending a cleartext command that is processed after TLS is in place, related to a "plaintext command injection" attack. |
| CVE-2010-4643 | High | 2011-01-28 | Not applicable | No public exploit | Heap-based buffer overflow in Impress in OpenOffice.org (OOo) 2.x and 3.x before 3.3 allows remote attackers to cause a denial of service (application crash) or possibly execute arbitrary code via a crafted Truevision TGA (TARGA) file in an ODF or Microsoft Office document. |
| CVE-2010-4253 | High | 2011-01-28 | Not applicable | No public exploit | Heap-based buffer overflow in Impress in OpenOffice.org (OOo) 2.x and 3.x before 3.3 allows remote attackers to cause a denial of service (application crash) or possibly execute arbitrary code via a crafted PNG file in an ODF or Microsoft Office document, as demonstrated by a PowerPoint (aka PPT) document. |
| CVE-2010-3689 | Medium | 2011-01-28 | Not applicable | No public exploit | soffice in OpenOffice.org (OOo) 3.x before 3.3 places a zero-length directory name in the LD_LIBRARY_PATH, which allows local users to gain privileges via a Trojan horse shared library in the current working directory. |
| CVE-2010-3454 | High | 2011-01-28 | Not applicable | No public exploit | Multiple off-by-one errors in the WW8DopTypography::ReadFromMem function in oowriter in OpenOffice.org (OOo) 2.x and 3.x before 3.3 allow remote attackers to cause a denial of service (application crash) or possibly execute arbitrary code via crafted typography information in a Microsoft Word .DOC file that triggers an out-of-bounds write. |
| CVE-2010-3453 | High | 2011-01-28 | Not applicable | No public exploit | The WW8ListManager::WW8ListManager function in oowriter in OpenOffice.org (OOo) 2.x and 3.x before 3.3 does not properly handle an unspecified number of list levels in user-defined list styles in WW8 data in a Microsoft Word document, which allows remote attackers to cause a denial of service (application crash) or possibly execute arbitrary code via a crafted .DOC file that triggers an out-of-bounds write. |
| CVE-2010-3452 | High | 2011-01-28 | Not applicable | No public exploit | Use-after-free vulnerability in oowriter in OpenOffice.org (OOo) 2.x and 3.x before 3.3 allows remote attackers to cause a denial of service (application crash) or possibly execute arbitrary code via crafted tags in an RTF document. |
| CVE-2010-3451 | High | 2011-01-28 | Not applicable | No public exploit | Use-after-free vulnerability in oowriter in OpenOffice.org (OOo) 2.x and 3.x before 3.3 allows remote attackers to cause a denial of service (application crash) or possibly execute arbitrary code via malformed tables in an RTF document. |
| CVE-2010-3450 | High | 2011-01-28 | Not applicable | No public exploit | Multiple directory traversal vulnerabilities in OpenOffice.org (OOo) 2.x and 3.x before 3.3 allow remote attackers to overwrite arbitrary files via a .. (dot dot) in an entry in (1) an XSLT JAR filter description file, (2) an Extension (aka OXT) file, or unspecified other (3) JAR or (4) ZIP files. |