
Oracle Critical Patch Update April 2011
Released April 2011 · Oracle's advisory ↗ · ← Java SE Critical Patch Update, February 2011 · Java SE Critical Patch Update, June 2011 →
72 CVEs in this release, one square each
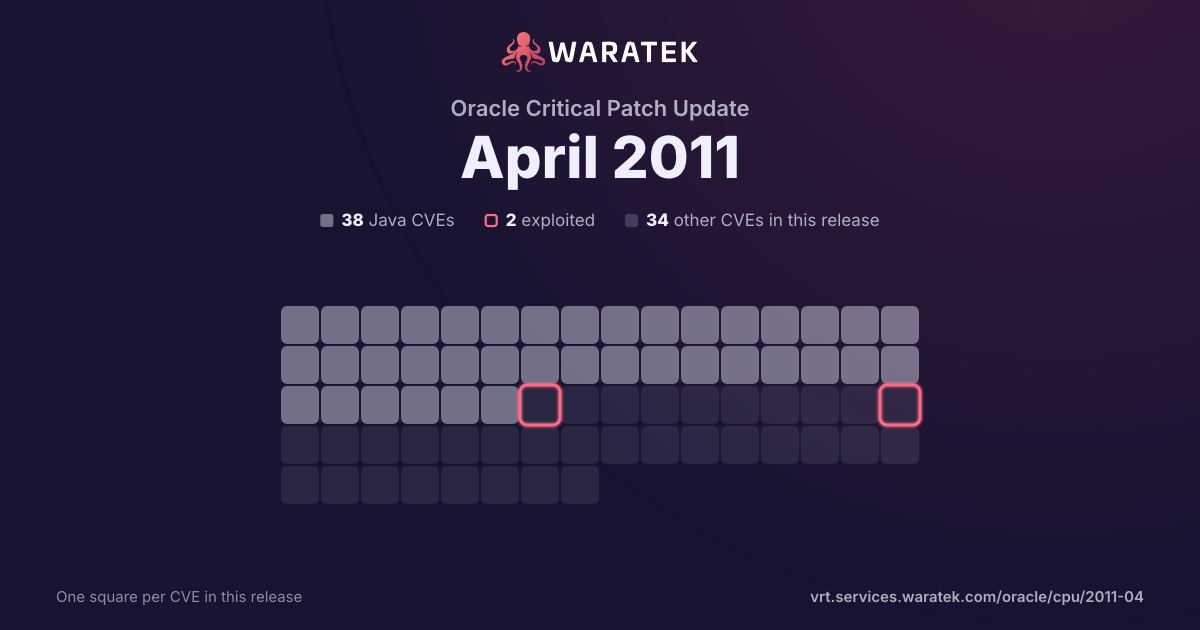
By status
4Mitigation candidate37No exploit published7Outside Waratek scope24Not applicable
2Exploited, marked by the ring
No exploit published. For 37 of them, Oracle's security advisory is the source of public detail.
Overview 2 matches · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
2matches
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
2
100.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
2
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
2
100.0%
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2011-0827 | Low | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise component in Oracle PeopleSoft Products 8.50 GA through 8.50.17 and 8.51 GA through 8.51.07 allows remote authenticated users to affect integrity via unknown vectors related to PeopleTools. |
| CVE-2011-0826 | Low | 2011-04-20 | No exploit published | No public exploit | Unspecified vulnerability in Oracle PeopleSoft Enterprise 8.8 Bundle #13, 8.9 Bundle #7, 9.0 Bundle #7, and 9.1 Bundle #4 allows remote authenticated users to affect integrity via unknown vectors related to Application Portal. |