
Oracle Critical Patch Update April 2011
Released April 2011 · Oracle's advisory ↗ · ← Java SE Critical Patch Update, February 2011 · Java SE Critical Patch Update, June 2011 →
72 CVEs in this release, one square each
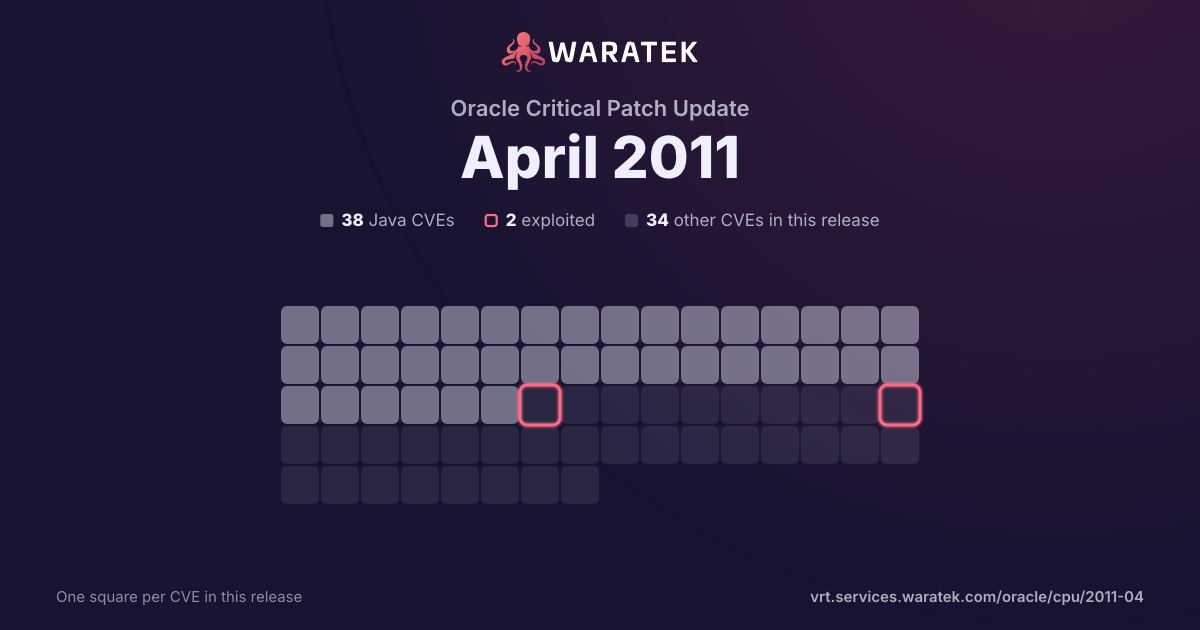
By status
4Mitigation candidate37No exploit published7Outside Waratek scope24Not applicable
2Exploited, marked by the ring
No exploit published. For 37 of them, Oracle's security advisory is the source of public detail.
Overview 2 matches · 0 protected · 1 exploited · 0 CISA KEV
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
2
100.0%
No exploit published
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
2
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
50.0%
Working exploit published
1
50.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 1 / month
Dec 09Feb 10Apr 10Jun 10Aug 10Oct 10Dec 10Feb 11Apr 11
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2011-0807 | High | 2011-04-20 | Mitigation candidate | Working exploit published | Unspecified vulnerability in Oracle Sun GlassFish Enterprise Server 2.1, 2.1.1, and 3.0.1, and Sun Java System Application Server 9.1, allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Administration. |
| CVE-2009-3555 | Critical | 2009-11-09 | Mitigation candidate | Exploited | The TLS protocol, and the SSL protocol 3.0 and possibly earlier, as used in Microsoft Internet Information Services (IIS) 7.0, mod_ssl in the Apache HTTP Server 2.2.14 and earlier, OpenSSL before 0.9.8l, GnuTLS 2.8.5 and earlier, Mozilla Network Security Services (NSS) 3.12.4 and earlier, multiple Cisco products, and other products, does not properly associate renegotiation handshakes with an existing connection, which allows man-in-the-middle attackers to insert data into HTTPS sessions, and possibly other types of sessions protected by TLS or SSL, by sending an unauthenticated request that is processed retroactively by a server in a post-renegotiation context, related to a "plaintext injection" attack, aka the "Project Mogul" issue. |