
Oracle Critical Patch Update January 2011
Released January 2011 · Oracle's advisory ↗ · ← Java SE Critical Patch Update, October 2010 · Java SE Critical Patch Update, February 2011 →
66 CVEs in this release, one square each
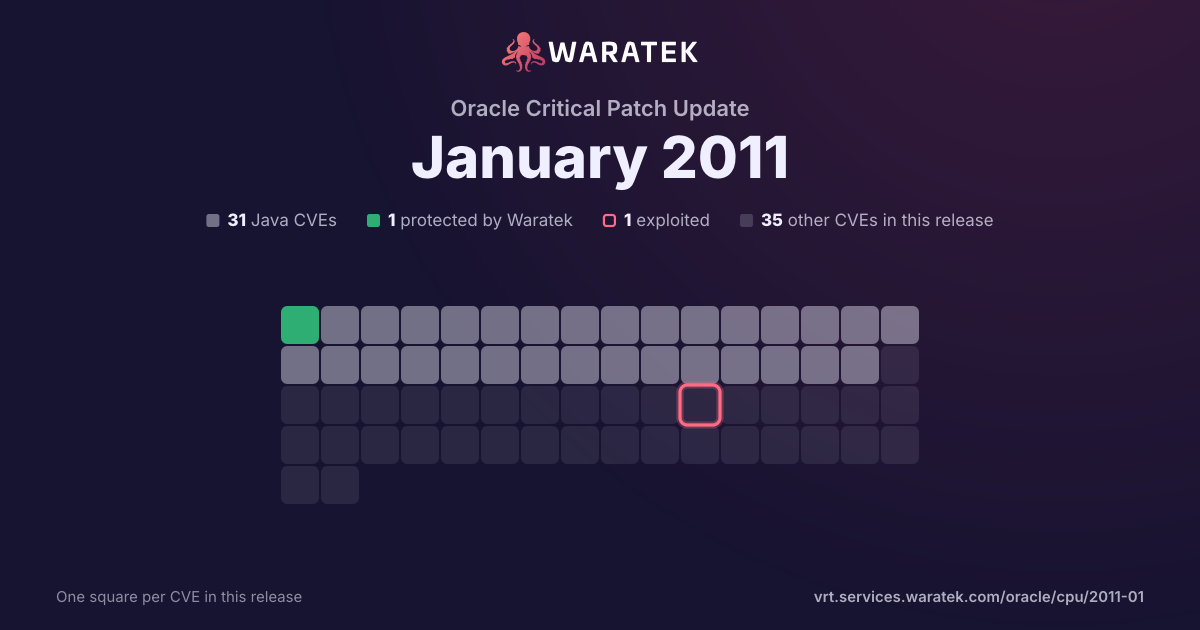
By status
1Protected by Waratek3Mitigation candidate27No exploit published11Outside Waratek scope24Not applicable
1Exploited, marked by the ring
No exploit published. For 26 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 3 matches · 0 protected · 0 exploited · 0 CISA KEV · 1 EPSS ≥ 0.5
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
3
100.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
0
0.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
3
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
3
100.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 3 / month
Jan 11
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2010-4437 | Medium | 2011-01-19 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 9.0, 9.1, 9.2.4, 10.0.2, 10.3.2, and 10.3.3 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Servlet Container. |
| CVE-2010-4417 | High | 2011-01-19 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Services for Beehive component in Oracle Fusion Middleware 2.0.1.0, 2.0.1.1, 2.0.1.2, 2.0.1.2.1, and 2.0.1.3 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. NOTE: the previous information was obtained from the January 2011 CPU. Oracle has not commented on claims from a reliable third party coordinator that voice-servlet/prompt-qa/Index.jspf does not properly handle null (%00) bytes in the evaluation parameter that is used in a filename, which allows attackers to create a file with an executable extension and execute arbitrary JSP code. |
| CVE-2010-3595 | High | 2011-01-19 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Oracle Document Capture component in Oracle Fusion Middleware 10.1.3.4 and 10.1.3.5 allows remote attackers to affect confidentiality via unknown vectors related to Import Server. NOTE: the previous information was obtained from the January 2011 CPU. Oracle has not commented on claims from the original researcher that remote attackers can read arbitrary files via a full pathname in the first argument to the ImportBodyText method in the EasyMail ActiveX control (emsmtp.dll). |