
Oracle Critical Patch Update January 2011
Released January 2011 · Oracle's advisory ↗ · ← Java SE Critical Patch Update, October 2010 · Java SE Critical Patch Update, February 2011 →
66 CVEs in this release, one square each
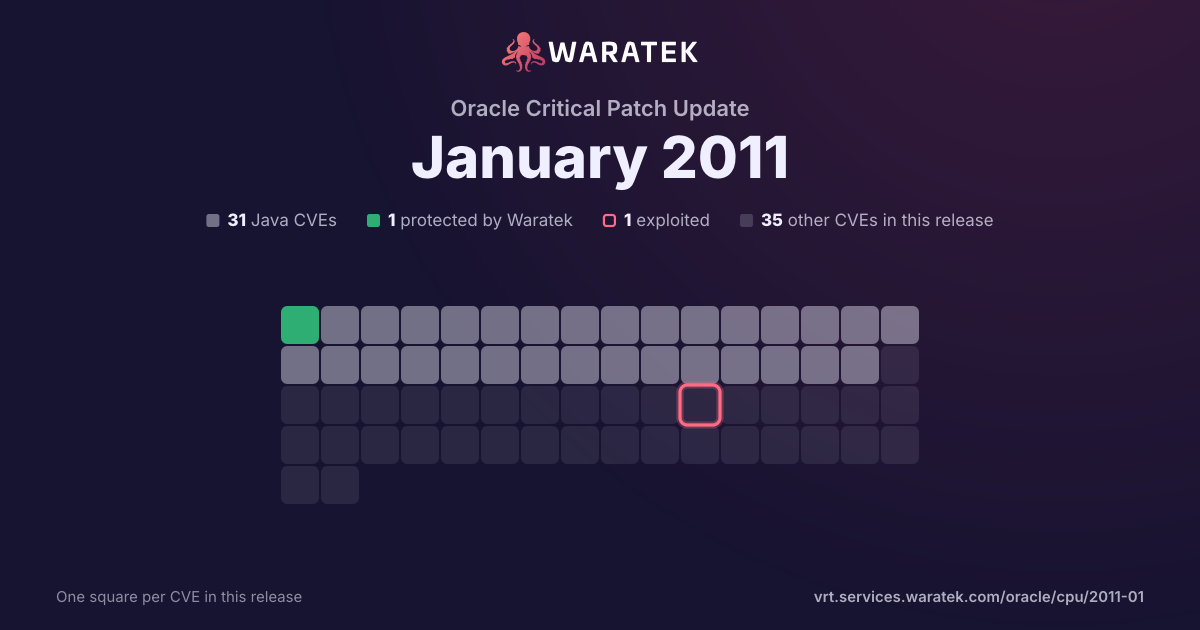
By status
1Protected by Waratek3Mitigation candidate27No exploit published11Outside Waratek scope24Not applicable
1Exploited, marked by the ring
No exploit published. For 26 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 14 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
14matches
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
14
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
14
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
14
100.0%
split by
peak 13 / month
Apr 10May 10Jun 10Jul 10Aug 10Sep 10Oct 10Nov 10Dec 10Jan 11
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2010-4464 | Medium | 2011-01-19 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Convergence 1.0 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Webmail. |
| CVE-2010-4459 | Medium | 2011-01-19 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 11 Express allows local users to affect availability via unknown vectors related to SCTP and Kernel/sockfs. |
| CVE-2010-4458 | Medium | 2011-01-19 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 11 Express allows local users to affect availability, related to ZFS. |
| CVE-2010-4456 | Medium | 2011-01-19 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Java System Communications Express 6.2 and 6.3 allows remote attackers to affect integrity via unknown vectors related to Web Mail. |
| CVE-2010-4446 | Medium | 2011-01-19 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 11 Express allows local users to affect availability via unknown vectors related to RDS and Kernel/InfiniBand. |
| CVE-2010-4444 | Medium | 2011-01-19 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Java System Access Manager and Oracle OpenSSO 7, 7.1, and 8 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2010-4443 | Medium | 2011-01-19 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and 11 Express allows local users to affect availability, related to Kernel/NFS. |
| CVE-2010-4442 | Medium | 2011-01-19 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and 11 Express allows local users to affect availability via unknown vectors related to the Kernel. |
| CVE-2010-4440 | Medium | 2011-01-19 | Not applicable | No public exploit | Unspecified vulnerability in Oracle 10 and 11 Express allows local users to affect availability via unknown vectors related to the Kernel. |
| CVE-2010-4436 | Medium | 2011-01-19 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Management Center (SunMC) 4.0 allows remote attackers to affect confidentiality via unknown vectors related to Web Console. |
| CVE-2010-4433 | Medium | 2011-01-19 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 allows remote attackers to affect confidentiality via unknown vectors related to Ethernet and the Driver sub-component. |
| CVE-2010-4415 | Medium | 2011-01-19 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 8, 9, and 10 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to libc. |
| CVE-2010-4414 | Medium | 2011-01-19 | Not applicable | No public exploit | Unspecified vulnerability in Oracle VM VirtualBox 4.0 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Extensions. |
| CVE-2010-1227 | Medium | 2010-04-01 | Not applicable | No public exploit | Cross-site scripting (XSS) vulnerability in Sun Java System Communications Express 6.2 and 6.3 allows remote attackers to inject arbitrary web script or HTML via the subject field of a message, as demonstrated by a subject containing an IMG element with a SRC attribute that performs a cross-site request forgery (CSRF) attack involving the cmd and argv parameters to cmd.msc. |