
Oracle Critical Patch Update January 2011
Released January 2011 · Oracle's advisory ↗ · ← Java SE Critical Patch Update, October 2010 · Java SE Critical Patch Update, February 2011 →
66 CVEs in this release, one square each
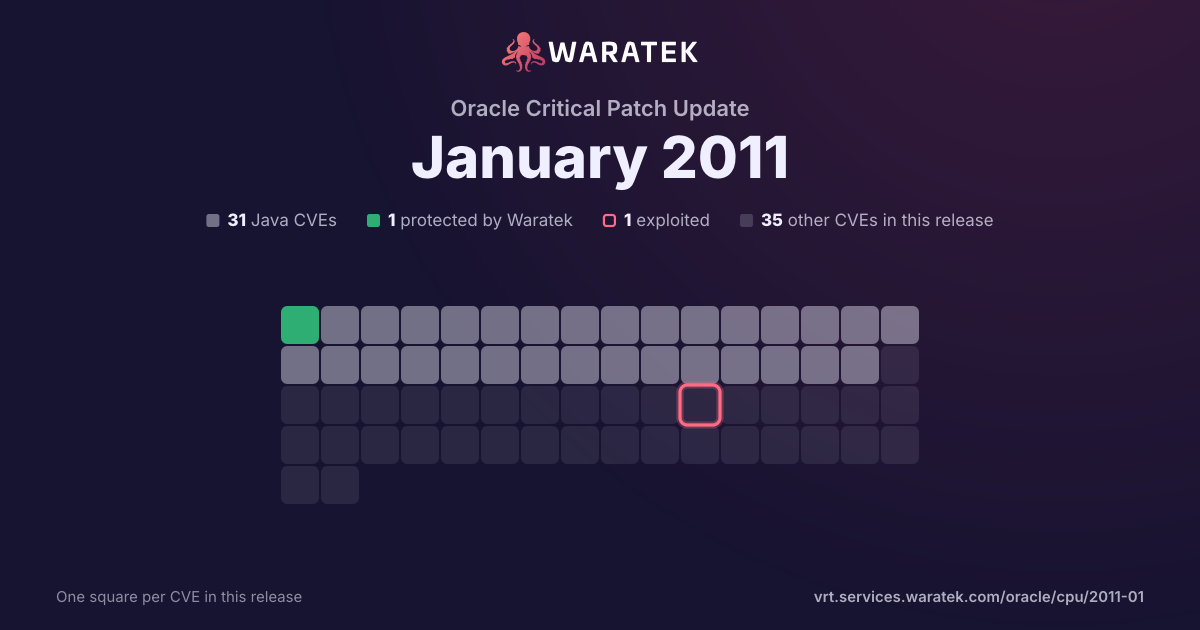
By status
1Protected by Waratek3Mitigation candidate27No exploit published11Outside Waratek scope24Not applicable
1Exploited, marked by the ring
No exploit published. For 26 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 6 matches · 1 in Waratek scope · 0 protected · 1 exploited · 0 CISA KEV · 1 public PoC · 1 EPSS ≥ 0.5
6matches
1in Waratek scope16.7%
0protected0.0%
1exploited16.7%
0CISA KEV0.0%
1public PoC16.7%
1EPSS ≥ 0.516.7%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
1
16.7%
Outside Waratek scope
1
16.7%
Not applicable
4
66.7%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
6
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
16.7%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
5
83.3%
split by
peak 3 / month
Nov 091
Not applicable1
Critical1
not blocked1
Exploited1
Dec 090
Jan 100
Feb 100
Mar 100
Apr 101
Not applicable1
Medium1
not blocked1
No public exploit1
May 100
Jun 100
Jul 100
Aug 103
No exploit published1
Not applicable2
High2
Low1
not blocked3
No public exploit3
Sep 100
Oct 101
Outside Waratek scope1
High1
not blocked1
No public exploit1
Nov 09Dec 09Jan 10Feb 10Mar 10Apr 10May 10Jun 10Jul 10Aug 10Sep 10Oct 10
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2010-3574 | High | 2010-10-19 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Networking component in Oracle Java SE and Java for Business 6 Update 21, 5.0 Update 25, 1.4.2_27, and 1.3.1_28 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. NOTE: the previous information was obtained from the October 2010 CPU. Oracle has not commented on claims from a reliable downstream vendor that HttpURLConnection does not properly check for the allowHttpTrace permission, which allows untrusted code to perform HTTP TRACE requests. |
| CVE-2010-2936 | High | 2010-08-25 | Not applicable | No public exploit | Integer overflow in simpress.bin in the Impress module in OpenOffice.org (OOo) 2.x and 3.x before 3.3 allows remote attackers to cause a denial of service (application crash) or possibly execute arbitrary code via crafted polygons in a PowerPoint document that triggers a heap-based buffer overflow. |
| CVE-2010-2935 | High | 2010-08-25 | Not applicable | No public exploit | simpress.bin in the Impress module in OpenOffice.org (OOo) 2.x and 3.x before 3.3 does not properly handle integer values associated with dictionary property items, which allows remote attackers to cause a denial of service (application crash) or possibly execute arbitrary code via a crafted PowerPoint document that triggers a heap-based buffer overflow, related to an "integer truncation error." |
| CVE-2009-4269 | Low | 2010-08-16 | No exploit published | No public exploit | The password hash generation algorithm in the BUILTIN authentication functionality for Apache Derby before 10.6.1.0 performs a transformation that reduces the size of the set of inputs to SHA-1, which produces a small search space that makes it easier for local and possibly remote attackers to crack passwords by generating hash collisions, related to password substitution. |
| CVE-2010-1227 | Medium | 2010-04-01 | Not applicable | No public exploit | Cross-site scripting (XSS) vulnerability in Sun Java System Communications Express 6.2 and 6.3 allows remote attackers to inject arbitrary web script or HTML via the subject field of a message, as demonstrated by a subject containing an IMG element with a SRC attribute that performs a cross-site request forgery (CSRF) attack involving the cmd and argv parameters to cmd.msc. |
| CVE-2009-3555 | Critical | 2009-11-09 | Not applicable | Exploited | The TLS protocol, and the SSL protocol 3.0 and possibly earlier, as used in Microsoft Internet Information Services (IIS) 7.0, mod_ssl in the Apache HTTP Server 2.2.14 and earlier, OpenSSL before 0.9.8l, GnuTLS 2.8.5 and earlier, Mozilla Network Security Services (NSS) 3.12.4 and earlier, multiple Cisco products, and other products, does not properly associate renegotiation handshakes with an existing connection, which allows man-in-the-middle attackers to insert data into HTTPS sessions, and possibly other types of sessions protected by TLS or SSL, by sending an unauthenticated request that is processed retroactively by a server in a post-renegotiation context, related to a "plaintext injection" attack, aka the "Project Mogul" issue. |