
Oracle Critical Patch Update January 2011
Released January 2011 · Oracle's advisory ↗ · ← Java SE Critical Patch Update, October 2010 · Java SE Critical Patch Update, February 2011 →
66 CVEs in this release, one square each
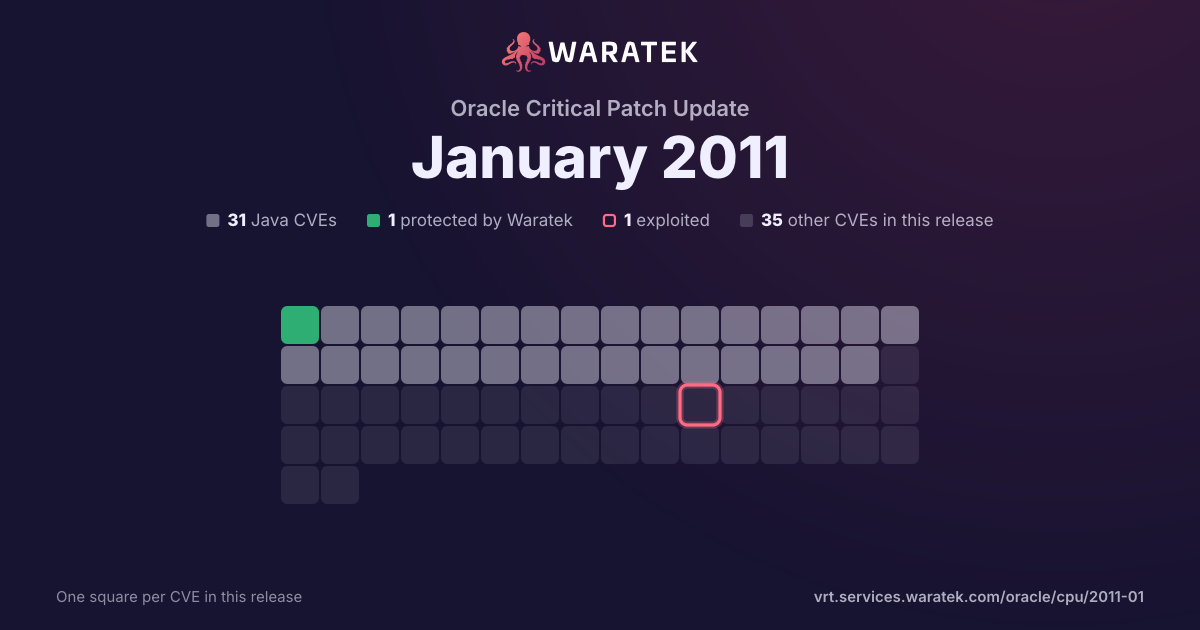
By status
1Protected by Waratek3Mitigation candidate27No exploit published11Outside Waratek scope24Not applicable
1Exploited, marked by the ring
No exploit published. For 26 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 17 matches · 5 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 7 public PoC · 2 EPSS ≥ 0.5
17matches
5in Waratek scope29.4%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
7public PoC41.2%
2EPSS ≥ 0.511.8%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
2
11.8%
No exploit published
3
17.6%
Outside Waratek scope
6
35.3%
Not applicable
6
35.3%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
17
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
7
41.2%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
10
58.8%
split by
peak 14 / month
Aug 102
Not applicable2
High2
not blocked2
No public exploit2
Sep 100
Oct 101
Outside Waratek scope1
High1
not blocked1
No public exploit1
Nov 100
Dec 100
Jan 1114
Mitigation candidate2
No exploit published3
Outside Waratek scope5
Not applicable4
High14
not blocked14
Working exploit published7
No public exploit7
Aug 10Sep 10Oct 10Nov 10Dec 10Jan 11
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2010-4457 | High | 2011-01-19 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 11 Express allows remote attackers to affect availability, related to SMB and CIFS. |
| CVE-2010-4449 | High | 2011-01-19 | Not applicable | No public exploit | Unspecified vulnerability in the Audit Vault component in Oracle Audit Vault 10.2.3.2 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. NOTE: the previous information was obtained from the January 2011 CPU. Oracle has not commented on claims from a reliable third party coordinator that this issue is related to a crafted parameter in an action.execute request to the av component on TCP port 5700. |
| CVE-2010-4435 | High | 2011-01-19 | Not applicable | Working exploit published | Unspecified vulnerability in Oracle Solaris 8, 9, and 10 allows remote attackers to affect confidentiality, integrity, and availability, related to CDE Calendar Manager Service Daemon and RPC. NOTE: the previous information was obtained from the January 2011 CPU. Oracle has not commented on claims from other software vendors that this affects other operating systems, such as HP-UX, or claims from a reliable third party that this is a buffer overflow in rpc.cmsd via long XDR-encoded ASCII strings in RPC call 10. |
| CVE-2010-4418 | High | 2011-01-19 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft and JDEdwards Suite 8.50.11 through 8.50.15 and 8.51GA through 8.51.05 allows remote attackers to affect confidentiality, integrity, and availability, related to PIA Core Technology. |
| CVE-2010-4417 | High | 2011-01-19 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Services for Beehive component in Oracle Fusion Middleware 2.0.1.0, 2.0.1.1, 2.0.1.2, 2.0.1.2.1, and 2.0.1.3 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. NOTE: the previous information was obtained from the January 2011 CPU. Oracle has not commented on claims from a reliable third party coordinator that voice-servlet/prompt-qa/Index.jspf does not properly handle null (%00) bytes in the evaluation parameter that is used in a filename, which allows attackers to create a file with an executable extension and execute arbitrary JSP code. |
| CVE-2010-3600 | High | 2011-01-19 | Outside Waratek scope | Working exploit published | Unspecified vulnerability in the Client System Analyzer component in Oracle Database Server 11.1.0.7 and 11.2.0.1 and Enterprise Manager Grid Control 10.2.0.5 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. NOTE: the previous information was obtained from the January 2011 CPU. Oracle has not commented on claims from a reliable third party coordinator that this issue involves an exposed JSP script that accepts XML uploads in conjunction with NULL bytes in an unspecified parameter that allow execution of arbitrary code. |
| CVE-2010-3599 | High | 2011-01-19 | Outside Waratek scope | Working exploit published | Unspecified vulnerability in the Oracle Document Capture component in Oracle Fusion Middleware 10.1.3.4 and 10.1.3.5 allows remote attackers to affect integrity and availability via unknown vectors related to Import Server. NOTE: the previous information was obtained from the January 2011 CPU. Oracle has not commented on claims from the original researcher that remote attackers can overwrite arbitrary files and execute arbitrary code via a full pathname in the first argument to the WriteJPG method in the NCSECWLib ActiveX control. |
| CVE-2010-3598 | High | 2011-01-19 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Oracle Document Capture component in Oracle Fusion Middleware 10.1.3.4 and 10.1.3.5 allows remote attackers to affect integrity via unknown vectors related to Import Export Utility. |
| CVE-2010-3595 | High | 2011-01-19 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Oracle Document Capture component in Oracle Fusion Middleware 10.1.3.4 and 10.1.3.5 allows remote attackers to affect confidentiality via unknown vectors related to Import Server. NOTE: the previous information was obtained from the January 2011 CPU. Oracle has not commented on claims from the original researcher that remote attackers can read arbitrary files via a full pathname in the first argument to the ImportBodyText method in the EasyMail ActiveX control (emsmtp.dll). |
| CVE-2010-3593 | High | 2011-01-19 | No exploit published | No public exploit | Unspecified vulnerability in the Health Sciences - Oracle Argus Safety component in Oracle Industry Applications 5.0, 5.0.1, 5.0.2, and 5.0.3 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Login and LDAP. |
| CVE-2010-3592 | High | 2011-01-19 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Oracle Document Capture component in Oracle Fusion Middleware 10.1.3.4 and 10.1.3.5 allows remote attackers to affect integrity and availability via unknown vectors related to Internal Operations. |
| CVE-2010-3591 | High | 2011-01-19 | Outside Waratek scope | Working exploit published | Unspecified vulnerability in the Oracle Document Capture component in Oracle Fusion Middleware 10.1.3.4 and 10.1.3.5 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Internal Operations. NOTE: the previous information was obtained from the January 2011 CPU. Oracle has not commented on claims from the original researcher that remote attackers can overwrite or delete arbitrary files via a full pathname in the second argument to the DownloadSingleMessageToFile method in the EMPOP3Lib ActiveX component (empop3.dll). |
| CVE-2010-3510 | High | 2011-01-19 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 9.0, 9.1, 9.2.3, 10.0.2, 10.3.2, and 10.3.3 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Node Manager. |
| CVE-2010-2632 | High | 2011-01-19 | Not applicable | Working exploit published | Unspecified vulnerability in the FTP Server in Oracle Solaris 8, 9, 10, and 11 Express allows remote attackers to affect availability. NOTE: the previous information was obtained from the January 2011 CPU. Oracle has not commented on claims from a reliable researcher that this is an issue in the glob implementation in libc that allows remote authenticated users to cause a denial of service (CPU and memory consumption) via crafted glob expressions that do not match any pathnames. |
| CVE-2010-3574 | High | 2010-10-19 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Networking component in Oracle Java SE and Java for Business 6 Update 21, 5.0 Update 25, 1.4.2_27, and 1.3.1_28 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. NOTE: the previous information was obtained from the October 2010 CPU. Oracle has not commented on claims from a reliable downstream vendor that HttpURLConnection does not properly check for the allowHttpTrace permission, which allows untrusted code to perform HTTP TRACE requests. |
| CVE-2010-2936 | High | 2010-08-25 | Not applicable | No public exploit | Integer overflow in simpress.bin in the Impress module in OpenOffice.org (OOo) 2.x and 3.x before 3.3 allows remote attackers to cause a denial of service (application crash) or possibly execute arbitrary code via crafted polygons in a PowerPoint document that triggers a heap-based buffer overflow. |
| CVE-2010-2935 | High | 2010-08-25 | Not applicable | No public exploit | simpress.bin in the Impress module in OpenOffice.org (OOo) 2.x and 3.x before 3.3 does not properly handle integer values associated with dictionary property items, which allows remote attackers to cause a denial of service (application crash) or possibly execute arbitrary code via a crafted PowerPoint document that triggers a heap-based buffer overflow, related to an "integer truncation error." |