
Oracle Critical Patch Update October 2010
Released October 2010 · Oracle's advisory ↗ · ← Critical Patch Update, July 2010 · Java SE Critical Patch Update, October 2010 →
85 CVEs in this release, one square each
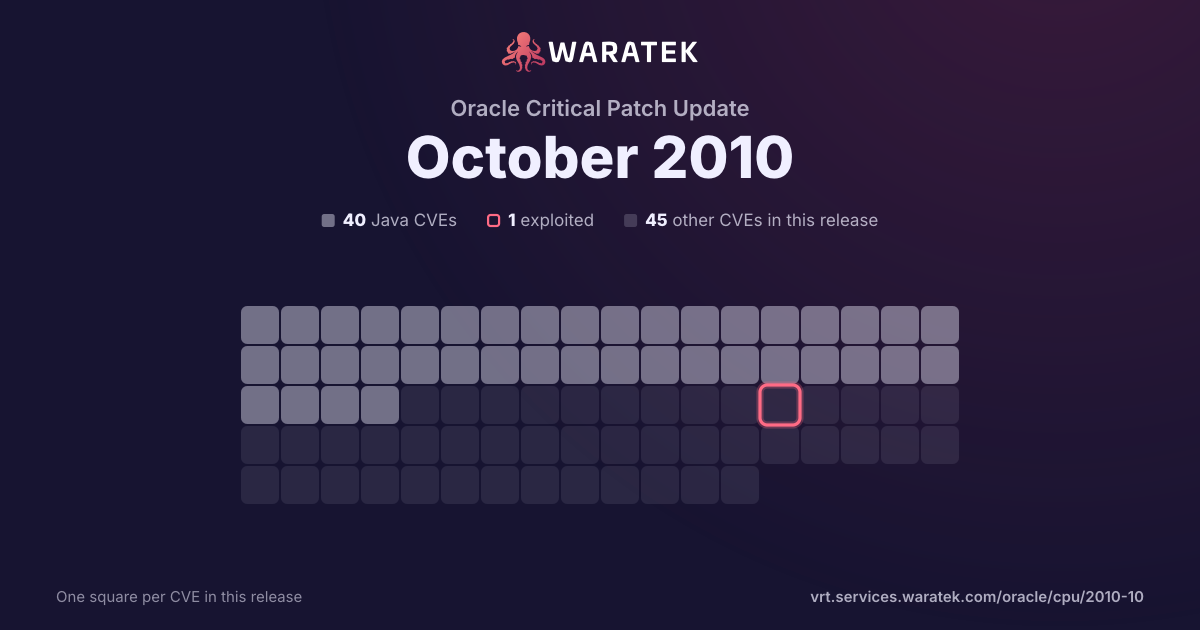
By status
1Mitigation candidate39No exploit published9Outside Waratek scope36Not applicable
1Exploited, marked by the ring
No exploit published. For 39 of them, Oracle's security advisory is the source of public detail.
Overview 36 matches · 0 in Waratek scope · 0 protected · 1 exploited · 0 CISA KEV · 4 public PoC · 2 EPSS ≥ 0.5
36matches
0in Waratek scope0.0%
0protected0.0%
1exploited2.8%
0CISA KEV0.0%
4public PoC11.1%
2EPSS ≥ 0.55.6%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
36
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
36
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
2.8%
Working exploit published
3
8.3%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
32
88.9%
split by
peak 30 / month
Nov 091
Not applicable1
Critical1
not blocked1
Exploited1
Dec 090
Jan 100
Feb 104
Not applicable4
High4
not blocked4
No public exploit4
Mar 100
Apr 100
May 100
Jun 101
Not applicable1
High1
not blocked1
No public exploit1
Jul 100
Aug 100
Sep 100
Oct 1030
Not applicable30
High5
Medium17
Low8
not blocked30
Working exploit published3
No public exploit27
Nov 09Dec 09Jan 10Feb 10Mar 10Apr 10May 10Jun 10Jul 10Aug 10Sep 10Oct 10
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2010-3585 | High | 2010-10-14 | Not applicable | Working exploit published | Unspecified vulnerability in the OracleVM component in Oracle VM 2.2.1 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors related to ovs-agent. NOTE: the previous information was obtained from the October 2010 CPU. Oracle has not commented on claims from a third party researcher that this is related to the exposure of unspecified functions using XML-RPC. |
| CVE-2010-3584 | Medium | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM component in Oracle VM 2.2.1 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to ovs-agent. NOTE: the previous information was obtained from the October 2010 CPU. Oracle has not commented on claims from a third party researcher that this is related to the storage of passwords and password hashes in cleartext in files with insecure permissions. |
| CVE-2010-3583 | High | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in the OracleVM component in Oracle VM 2.2.1 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors related to ovs-agent. NOTE: the previous information was obtained from the October 2010 CPU. Oracle has not commented on claims from a third party researcher that this is related to the exposure of multiple unspecified functions through XML-RPC that allow execution of arbitrary OS commands. |
| CVE-2010-3582 | High | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in the OracleVM component in Oracle VM 2.2.1 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors related to ovs-agent. |
| CVE-2010-3580 | Medium | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in Oracle OpenSolaris allows local users to affect availability via unknown vectors related to Kernel/File System. |
| CVE-2010-3579 | Medium | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in the (1) Sun Convergence 1 and (2) Sun Java Communications Suite 7 components in Oracle Sun Products Suite 1.0 and 7.0 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Webmail. |
| CVE-2010-3578 | High | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in Oracle OpenSolaris allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Depot Server. |
| CVE-2010-3577 | Medium | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in Oracle OpenSolaris allows remote attackers to affect confidentiality and integrity, related to Kernel/CIFS. |
| CVE-2010-3576 | Low | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 8, 9, and 10, and OpenSolaris, allows local users to affect integrity and availability, related to the SCSI enclosure services device driver. |
| CVE-2010-3575 | Medium | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Communications Messaging Server (Sun Java System Messaging Server) component in Oracle Sun Products Suite 6.0, 6.2, 6.3, and 7.0 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Web Mail. |
| CVE-2010-3564 | Medium | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Communications Messaging Server (Sun Java System Messaging Server) component in Oracle Sun Products Suite 7.0 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Webmail. NOTE: the previous information was obtained from the October 2010 CPU. Oracle has not commented on claims from a reliable downstream vendor that the Kerberos implementation does not properly check AP-REQ requests, which allows attackers to cause a denial of service in the JVM. NOTE: CVE has not investigated the apparent discrepancy between the two vendors regarding the consequences of this issue. |
| CVE-2010-3546 | Medium | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in the Sun Java System Identity Manager component in Oracle Sun Products Suite 8.1 allows remote attackers to affect confidentiality and integrity via unknown vectors. |
| CVE-2010-3545 | Medium | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle iPlanet Web Server (Sun Java System Web Server) component in Oracle Sun Products Suite 7.0 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Administration. |
| CVE-2010-3544 | Medium | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle iPlanet Web Server (Sun Java System Web Server) component in Oracle Sun Products Suite 7.0 allows remote attackers to affect integrity and availability via unknown vectors related to Administration. NOTE: the previous information was obtained from the October 2010 CPU. Oracle has not commented on claims from a reliable source that this is cross-site request forgery (CSRF) that allows remote attackers to stop an instance via the management console. |
| CVE-2010-3542 | Low | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 8, 9, and 10, and OpenSolaris, allows local users to affect confidentiality, related to USB. |
| CVE-2010-3540 | Medium | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and OpenSolaris allows local users to affect availability, related to ZFS. |
| CVE-2010-3535 | Medium | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in the Directory Server Enterprise Edition component in Oracle Sun Products Suite 6.0, 6.1, 6.2, and 6.3 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Identity Synchronization for Windows. |
| CVE-2010-3517 | Medium | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and OpenSolaris allows local users to affect availability, related to Kernel/X86. |
| CVE-2010-3516 | Medium | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and OpenSolaris allows local users to affect availability via unknown vectors related to InfiniBand. |
| CVE-2010-3515 | Medium | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in the Solaris component in Oracle Solaris 9 and 10, and OpenSolaris, allows local users to affect availability via unknown vectors related to Kernel/Disk Driver. |
| CVE-2010-3514 | Medium | 2010-10-14 | Not applicable | Working exploit published | Unspecified vulnerability in the Oracle iPlanet Web Server (Sun Java System Web Server) component in Oracle Sun Products Suite 6.1 and 7.0 allows remote attackers to affect integrity via unknown vectors related to Web Container. |
| CVE-2010-3513 | Low | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 9 and 10, and OpenSolaris, allows local users to affect integrity and availability via unknown vectors related to Device Drivers. |
| CVE-2010-3512 | Low | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle iPlanet Web Server (Sun Java System Web Server) component in Oracle Sun Products Suite 7.0u8 allows remote authenticated users to affect confidentiality, related to DAV (WebDAV). |
| CVE-2010-3511 | Low | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in Oracle OpenSolaris allows local users to affect integrity and availability via unknown vectors related to Tooltalk. |
| CVE-2010-3509 | High | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 8, 9, and 10 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Scheduler. |
| CVE-2010-3508 | Low | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 allows local users to affect confidentiality and integrity via unknown vectors related to Solaris Zones. |
| CVE-2010-3507 | Medium | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 8, 9, and 10 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Live Upgrade. |
| CVE-2010-3506 | Low | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Explorer (Sun Explorer) component in Oracle Sun Products Suite 6.4 allows local users to affect confidentiality and integrity via unknown vectors. |
| CVE-2010-3503 | Medium | 2010-10-14 | Not applicable | Working exploit published | Unspecified vulnerability in Oracle Solaris 10 and OpenSolaris allows local users to affect confidentiality and integrity via unknown vectors related to su. |
| CVE-2010-2414 | Low | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in the (1) Sun Convergence 1 and (2) Sun Java Communications Suite 7 components in Oracle Sun Products Suite 1.0 and 7.0 allows remote attackers to affect confidentiality via unknown vectors. |
| CVE-2010-0395 | High | 2010-06-10 | Not applicable | No public exploit | OpenOffice.org 2.x and 3.0 before 3.2.1 allows user-assisted remote attackers to bypass Python macro security restrictions and execute arbitrary Python code via a crafted OpenDocument Text (ODT) file that triggers code execution when the macro directory structure is previewed. |
| CVE-2009-3302 | High | 2010-02-16 | Not applicable | No public exploit | filter/ww8/ww8par2.cxx in OpenOffice.org (OOo) before 3.2 allows remote attackers to cause a denial of service (application crash) or possibly execute arbitrary code via a crafted sprmTSetBrc table property modifier in a Word document, related to a "boundary error flaw." |
| CVE-2009-3301 | High | 2010-02-16 | Not applicable | No public exploit | Integer underflow in filter/ww8/ww8par2.cxx in OpenOffice.org (OOo) before 3.2 allows remote attackers to cause a denial of service (application crash) or possibly execute arbitrary code via a crafted sprmTDefTable table property modifier in a Word document. |
| CVE-2009-2950 | High | 2010-02-16 | Not applicable | No public exploit | Heap-based buffer overflow in the GIFLZWDecompressor::GIFLZWDecompressor function in filter.vcl/lgif/decode.cxx in OpenOffice.org (OOo) before 3.2 allows remote attackers to cause a denial of service (application crash) or possibly execute arbitrary code via a crafted GIF file, related to LZW decompression. |
| CVE-2009-2949 | High | 2010-02-16 | Not applicable | No public exploit | Integer overflow in the XPMReader::ReadXPM function in filter.vcl/ixpm/svt_xpmread.cxx in OpenOffice.org (OOo) before 3.2 allows remote attackers to execute arbitrary code via a crafted XPM file that triggers a heap-based buffer overflow. |
| CVE-2009-3555 | Critical | 2009-11-09 | Not applicable | Exploited | The TLS protocol, and the SSL protocol 3.0 and possibly earlier, as used in Microsoft Internet Information Services (IIS) 7.0, mod_ssl in the Apache HTTP Server 2.2.14 and earlier, OpenSSL before 0.9.8l, GnuTLS 2.8.5 and earlier, Mozilla Network Security Services (NSS) 3.12.4 and earlier, multiple Cisco products, and other products, does not properly associate renegotiation handshakes with an existing connection, which allows man-in-the-middle attackers to insert data into HTTPS sessions, and possibly other types of sessions protected by TLS or SSL, by sending an unauthenticated request that is processed retroactively by a server in a post-renegotiation context, related to a "plaintext injection" attack, aka the "Project Mogul" issue. |