
Oracle Critical Patch Update October 2010
Released October 2010 · Oracle's advisory ↗ · ← Critical Patch Update, July 2010 · Java SE Critical Patch Update, October 2010 →
85 CVEs in this release, one square each
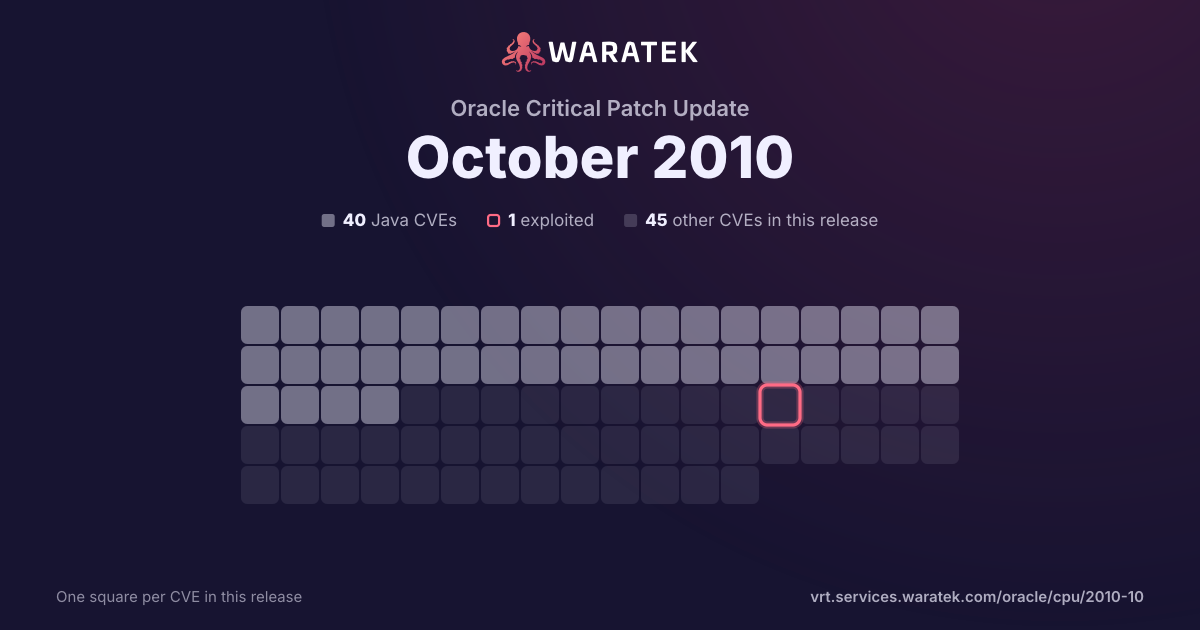
By status
1Mitigation candidate39No exploit published9Outside Waratek scope36Not applicable
1Exploited, marked by the ring
No exploit published. For 39 of them, Oracle's security advisory is the source of public detail.
Overview 10 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 1 EPSS ≥ 0.5
10matches
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
1public PoC10.0%
1EPSS ≥ 0.510.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
10
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
10
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
10.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
9
90.0%
split by
peak 5 / month
Feb 10Mar 10Apr 10May 10Jun 10Jul 10Aug 10Sep 10Oct 10
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2010-3585 | High | 2010-10-14 | Not applicable | Working exploit published | Unspecified vulnerability in the OracleVM component in Oracle VM 2.2.1 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors related to ovs-agent. NOTE: the previous information was obtained from the October 2010 CPU. Oracle has not commented on claims from a third party researcher that this is related to the exposure of unspecified functions using XML-RPC. |
| CVE-2010-3583 | High | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in the OracleVM component in Oracle VM 2.2.1 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors related to ovs-agent. NOTE: the previous information was obtained from the October 2010 CPU. Oracle has not commented on claims from a third party researcher that this is related to the exposure of multiple unspecified functions through XML-RPC that allow execution of arbitrary OS commands. |
| CVE-2010-3582 | High | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in the OracleVM component in Oracle VM 2.2.1 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors related to ovs-agent. |
| CVE-2010-3578 | High | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in Oracle OpenSolaris allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Depot Server. |
| CVE-2010-3509 | High | 2010-10-14 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 8, 9, and 10 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Scheduler. |
| CVE-2010-0395 | High | 2010-06-10 | Not applicable | No public exploit | OpenOffice.org 2.x and 3.0 before 3.2.1 allows user-assisted remote attackers to bypass Python macro security restrictions and execute arbitrary Python code via a crafted OpenDocument Text (ODT) file that triggers code execution when the macro directory structure is previewed. |
| CVE-2009-3302 | High | 2010-02-16 | Not applicable | No public exploit | filter/ww8/ww8par2.cxx in OpenOffice.org (OOo) before 3.2 allows remote attackers to cause a denial of service (application crash) or possibly execute arbitrary code via a crafted sprmTSetBrc table property modifier in a Word document, related to a "boundary error flaw." |
| CVE-2009-3301 | High | 2010-02-16 | Not applicable | No public exploit | Integer underflow in filter/ww8/ww8par2.cxx in OpenOffice.org (OOo) before 3.2 allows remote attackers to cause a denial of service (application crash) or possibly execute arbitrary code via a crafted sprmTDefTable table property modifier in a Word document. |
| CVE-2009-2950 | High | 2010-02-16 | Not applicable | No public exploit | Heap-based buffer overflow in the GIFLZWDecompressor::GIFLZWDecompressor function in filter.vcl/lgif/decode.cxx in OpenOffice.org (OOo) before 3.2 allows remote attackers to cause a denial of service (application crash) or possibly execute arbitrary code via a crafted GIF file, related to LZW decompression. |
| CVE-2009-2949 | High | 2010-02-16 | Not applicable | No public exploit | Integer overflow in the XPMReader::ReadXPM function in filter.vcl/ixpm/svt_xpmread.cxx in OpenOffice.org (OOo) before 3.2 allows remote attackers to execute arbitrary code via a crafted XPM file that triggers a heap-based buffer overflow. |