
Oracle Critical Patch Update July 2010
Released July 2010 · Oracle's advisory ↗ · ← Critical Patch Update, April 2010 · Critical Patch Update, October 2010 →
59 CVEs in this release, one square each
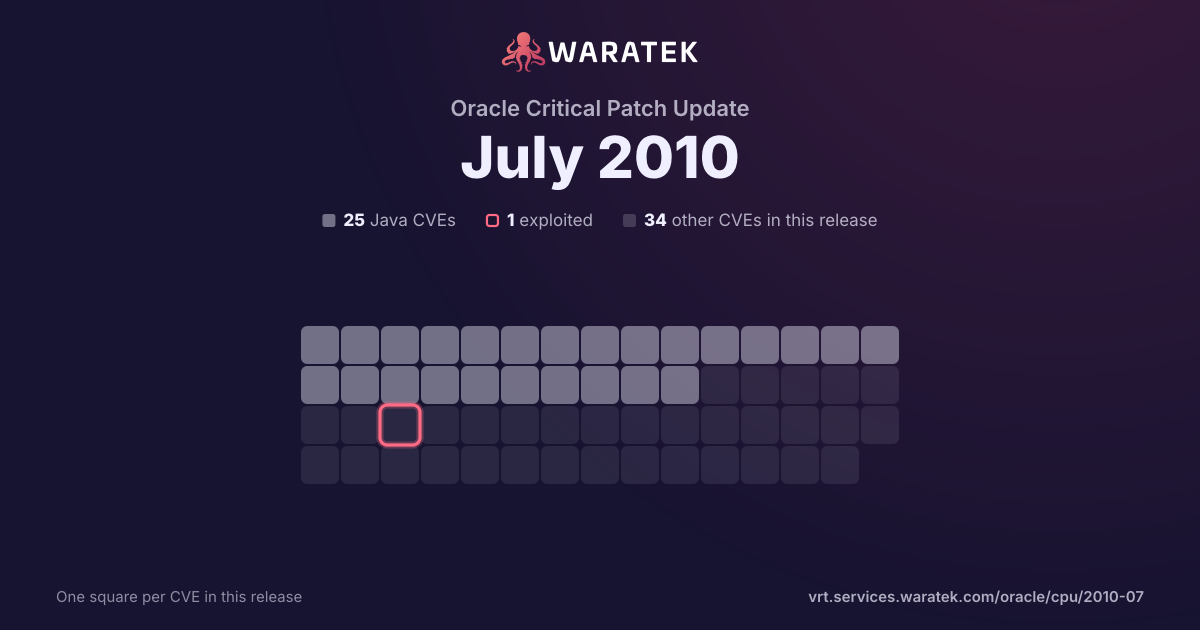
By status
2Mitigation candidate23No exploit published7Outside Waratek scope27Not applicable
1Exploited, marked by the ring
No exploit published. For 23 of them, Oracle's security advisory is the source of public detail.
Overview 2 matches · 0 in Waratek scope · 0 protected · 1 exploited · 0 CISA KEV · 1 EPSS ≥ 0.5
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
2
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
2
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
50.0%
Working exploit published
1
50.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 1 / month
Sep 08Nov 08Jan 09Mar 09May 09Jul 09Sep 09Nov 09
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2009-3555 | Critical | 2009-11-09 | Not applicable | Exploited | The TLS protocol, and the SSL protocol 3.0 and possibly earlier, as used in Microsoft Internet Information Services (IIS) 7.0, mod_ssl in the Apache HTTP Server 2.2.14 and earlier, OpenSSL before 0.9.8l, GnuTLS 2.8.5 and earlier, Mozilla Network Security Services (NSS) 3.12.4 and earlier, multiple Cisco products, and other products, does not properly associate renegotiation handshakes with an existing connection, which allows man-in-the-middle attackers to insert data into HTTPS sessions, and possibly other types of sessions protected by TLS or SSL, by sending an unauthenticated request that is processed retroactively by a server in a post-renegotiation context, related to a "plaintext injection" attack, aka the "Project Mogul" issue. |
| CVE-2008-4247 | High | 2008-09-25 | Not applicable | Working exploit published | ftpd in OpenBSD 4.3, FreeBSD 7.0, NetBSD 4.0, Solaris, and possibly other operating systems interprets long commands from an FTP client as multiple commands, which allows remote attackers to conduct cross-site request forgery (CSRF) attacks and execute arbitrary FTP commands via a long ftp:// URI that leverages an existing session from the FTP client implementation in a web browser. |