
Oracle Critical Patch Update July 2010
Released July 2010 · Oracle's advisory ↗ · ← Critical Patch Update, April 2010 · Critical Patch Update, October 2010 →
59 CVEs in this release, one square each
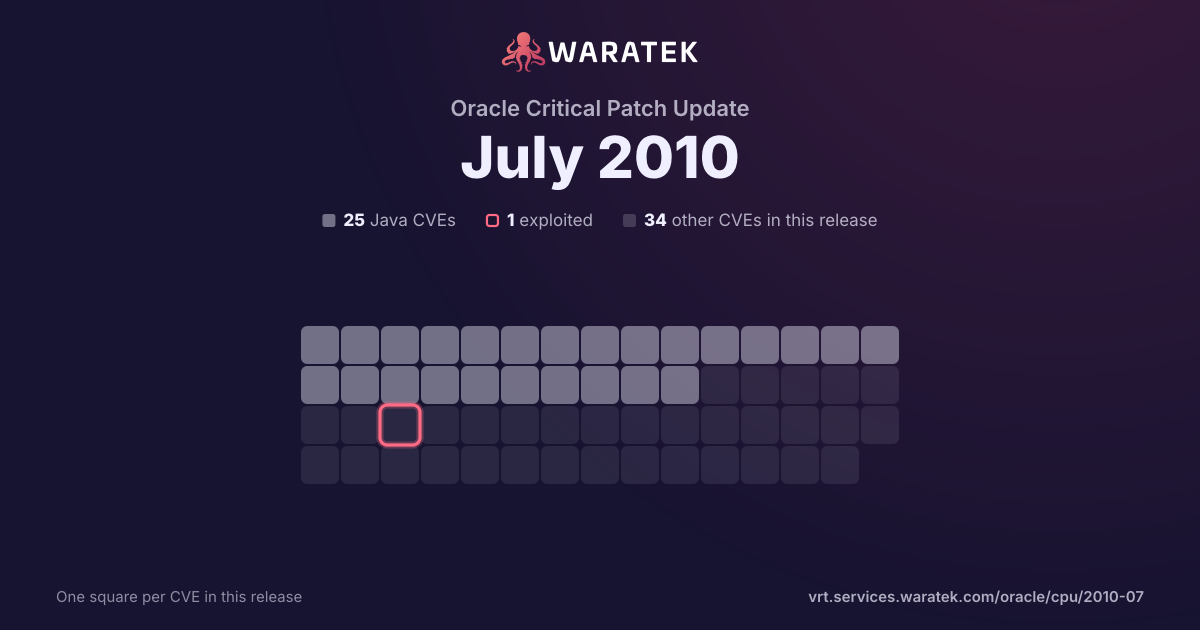
By status
3Mitigation candidate24No exploit published6Outside Waratek scope26Not applicable
1Exploited, marked by the ring
No exploit published. For 23 of them, Oracle's security advisory is the source of public detail.
Overview 7 matches · 0 protected · 1 exploited · 0 CISA KEV · 3 public PoC · 1 EPSS ≥ 0.5
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
3
42.9%
No exploit published
4
57.1%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
7
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
14.3%
Working exploit published
2
28.6%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
4
57.1%
split by
peak 5 / month
Nov 091
Mitigation candidate1
Critical1
not blocked1
Exploited1
Dec 090
Jan 100
Feb 100
Mar 100
Apr 101
No exploit published1
High1
not blocked1
No public exploit1
May 100
Jun 100
Jul 105
Mitigation candidate2
No exploit published3
Medium3
Low2
not blocked5
Working exploit published2
No public exploit3
Nov 09Dec 09Jan 10Feb 10Mar 10Apr 10May 10Jun 10Jul 10
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2010-2381 | Low | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the Application Server Control component in Oracle Fusion Middleware 10.1.2.3 and 10.1.4.0.1 allows remote authenticated users to affect integrity via unknown vectors, a different vulnerability than CVE-2010-0081. |
| CVE-2010-2375 | Medium | 2010-07-13 | Mitigation candidate | Working exploit published | Package/Privilege: Plugins for Apache, Sun and IIS web servers Unspecified vulnerability in the WebLogic Server component in Oracle Fusion Middleware 7.0 SP7, 8.1 SP6, 9.0, 9.1, 9.2 MP3, 10.0 MP2, 10.3.2, and 10.3.3 allows remote attackers to affect confidentiality and integrity, related to IIS. |
| CVE-2010-2370 | Medium | 2010-07-13 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Oracle Business Process Management component in Oracle Fusion Middleware 5.7 MP3, 6.0 MP5, and 10.3 MP2 allows remote attackers to affect integrity, related to BPM. |
| CVE-2010-0835 | Medium | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the Wireless component in Oracle Fusion Middleware 10.1.2.3 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2010-0081 | Low | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the Application Server Control component in Oracle Fusion Middleware 10.1.2.3 and 10.1.4.0.1 allows remote authenticated users to affect integrity via unknown vectors, a different vulnerability than CVE-2010-2381. |
| CVE-2010-0849 | High | 2010-04-01 | No exploit published | No public exploit | Unspecified vulnerability in the Java 2D component in Oracle Java SE and Java for Business 6 Update 18, 5.0 Update 23, 1.4.2_25, and 1.3.1_27 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. NOTE: the previous information was obtained from the March 2010 CPU. Oracle has not commented on claims from a reliable researcher that this is a heap-based buffer overflow in a decoding routine used by the JPEGImageDecoderImpl interface, which allows code execution via a crafted JPEG image. |
| CVE-2009-3555 | Critical | 2009-11-09 | Mitigation candidate | Exploited | The TLS protocol, and the SSL protocol 3.0 and possibly earlier, as used in Microsoft Internet Information Services (IIS) 7.0, mod_ssl in the Apache HTTP Server 2.2.14 and earlier, OpenSSL before 0.9.8l, GnuTLS 2.8.5 and earlier, Mozilla Network Security Services (NSS) 3.12.4 and earlier, multiple Cisco products, and other products, does not properly associate renegotiation handshakes with an existing connection, which allows man-in-the-middle attackers to insert data into HTTPS sessions, and possibly other types of sessions protected by TLS or SSL, by sending an unauthenticated request that is processed retroactively by a server in a post-renegotiation context, related to a "plaintext injection" attack, aka the "Project Mogul" issue. |