
Oracle Critical Patch Update July 2010
Released July 2010 · Oracle's advisory ↗ · ← Critical Patch Update, April 2010 · Critical Patch Update, October 2010 →
59 CVEs in this release, one square each
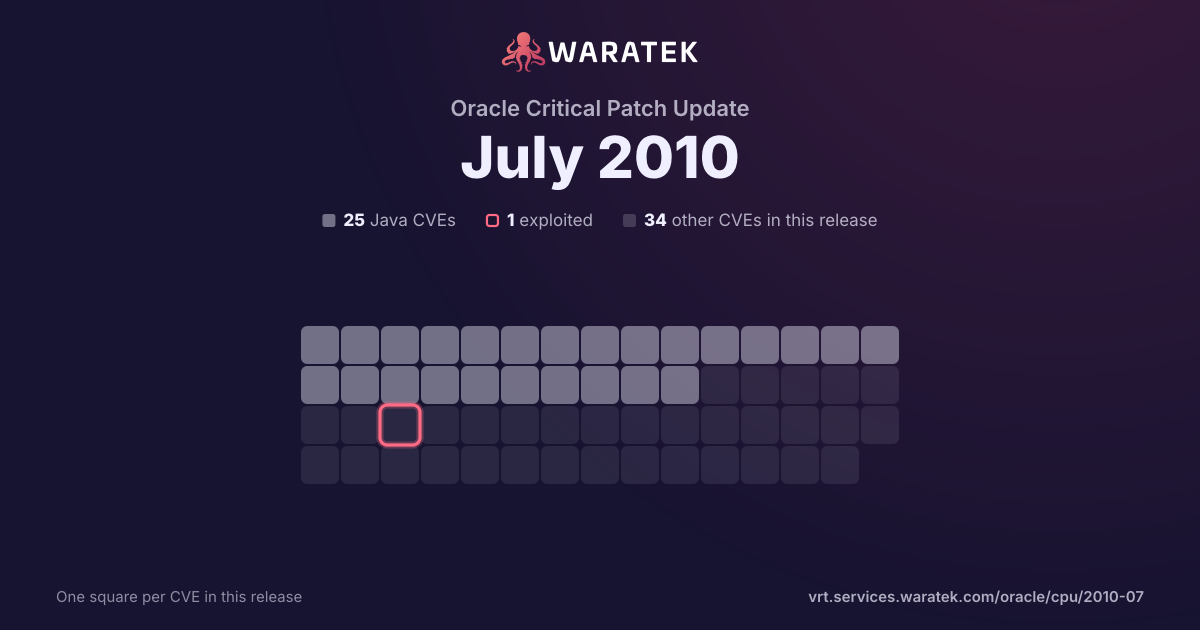
By status
3Mitigation candidate24No exploit published6Outside Waratek scope26Not applicable
1Exploited, marked by the ring
No exploit published. For 23 of them, Oracle's security advisory is the source of public detail.
Overview 58 matches · 27 in Waratek scope · 0 protected · 1 exploited · 0 CISA KEV · 8 public PoC · 2 EPSS ≥ 0.5
58matches
27in Waratek scope46.6%
0protected0.0%
1exploited1.7%
0CISA KEV0.0%
8public PoC13.8%
2EPSS ≥ 0.53.4%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
3
5.2%
No exploit published
24
41.4%
Outside Waratek scope
6
10.3%
Not applicable
25
43.1%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
58
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
1.7%
Working exploit published
7
12.1%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
50
86.2%
split by
peak 55 / month
Jul 091
No exploit published1
Medium1
not blocked1
No public exploit1
Aug 090
Sep 090
Oct 090
Nov 091
Mitigation candidate1
Critical1
not blocked1
Exploited1
Dec 090
Jan 100
Feb 100
Mar 100
Apr 101
No exploit published1
High1
not blocked1
No public exploit1
May 100
Jun 100
Jul 1055
Mitigation candidate2
No exploit published22
Outside Waratek scope6
Not applicable25
High9
Medium30
Low16
not blocked55
Working exploit published7
No public exploit48
Jul 09Sep 09Nov 09Jan 10Mar 10May 10Jul 10
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2010-2403 | Low | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise Campus Solutions component in Oracle PeopleSoft and JDEdwards Suite Campus Solutions 9.0 Bundle #17 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2010-2402 | Medium | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft and JDEdwards Suite 8.49.27 allows remote authenticated users to affect confidentiality and integrity via unknown vectors. |
| CVE-2010-2401 | Medium | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HCM - eProfile Mgr component in Oracle PeopleSoft and JDEdwards Suite HCM 9.0 Bundle #9 allows remote authenticated users to affect confidentiality and integrity via unknown vectors. |
| CVE-2010-2400 | Medium | 2010-07-13 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 9 and 10, and OpenSolaris, allows local users to affect availability via unknown vectors related to Kernel/Filesystem. |
| CVE-2010-2399 | Medium | 2010-07-13 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and OpenSolaris allows local users to affect availability via unknown vectors related to Kernel/VM. |
| CVE-2010-2398 | Medium | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HCM component in Oracle PeopleSoft and JDEdwards Suite HCM 9.0 Bundle #12 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2010-2397 | Low | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in Oracle Sun Java System Application Server 8.0, 8.1, and 8.2; and GlassFish Enterprise Server 2.1.1; allows local users to affect confidentiality and integrity, related to the GUI. |
| CVE-2010-2394 | Medium | 2010-07-13 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 allows local users to affect availability, related to TCP/IP. |
| CVE-2010-2393 | Low | 2010-07-13 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and OpenSolaris allows local users to affect availability, related to RPC. |
| CVE-2010-2392 | Medium | 2010-07-13 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and OpenSolaris allows local users to affect integrity and availability, related to ZFS. |
| CVE-2010-2386 | Medium | 2010-07-13 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 8, 9, and 10, and OpenSolaris, allows local users to affect availability via unknown vectors related to GigaSwift Ethernet Driver. |
| CVE-2010-2385 | Medium | 2010-07-13 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Java System Web Proxy Server 4.0.13 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Administration Server. |
| CVE-2010-2384 | Low | 2010-07-13 | Not applicable | Working exploit published | Unspecified vulnerability in Oracle Solaris 9 and 10 allows local users to affect confidentiality and integrity via unknown vectors related to Solaris Management Console. |
| CVE-2010-2383 | Low | 2010-07-13 | Not applicable | Working exploit published | Unspecified vulnerability in Oracle Solaris 8, 9, and 10, and OpenSolaris, allows local users to affect confidentiality and integrity, related to NFS. |
| CVE-2010-2382 | Low | 2010-07-13 | Not applicable | Working exploit published | Unspecified vulnerability in Oracle Solaris 8, 9, and 10 allows local users to affect confidentiality and integrity via unknown vectors. |
| CVE-2010-2381 | Low | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the Application Server Control component in Oracle Fusion Middleware 10.1.2.3 and 10.1.4.0.1 allows remote authenticated users to affect integrity via unknown vectors, a different vulnerability than CVE-2010-0081. |
| CVE-2010-2380 | Medium | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise FSCM component in Oracle PeopleSoft and JDEdwards Suite SCM 8.9 Bundle #37, SCM 9.0 Bundle #30, and SCM 9.1 Bundle #4 allows local users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2010-2379 | Medium | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HCM - Time & Labor component in Oracle PeopleSoft and JDEdwards Suite HCM 9.0 Bundle #13 and HCM 9.1 Bundle #2 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2010-2378 | Low | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise CRM component in Oracle PeopleSoft and JDEdwards Suite CRM 9.0 Bundle #28 and CRM 9.1 Bundle #4 allows local users to affect confidentiality and integrity via unknown vectors. |
| CVE-2010-2377 | Medium | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft and JDEdwards Suite 8.49.27 and 8.50.10 allows remote authenticated users to affect integrity via unknown vectors. |
| CVE-2010-2376 | Low | 2010-07-13 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 8, 9, and 10 allows local users to affect confidentiality and integrity via unknown vectors related to Solaris Management Console. |
| CVE-2010-2375 | Medium | 2010-07-13 | Mitigation candidate | Working exploit published | Package/Privilege: Plugins for Apache, Sun and IIS web servers Unspecified vulnerability in the WebLogic Server component in Oracle Fusion Middleware 7.0 SP7, 8.1 SP6, 9.0, 9.1, 9.2 MP3, 10.0 MP2, 10.3.2, and 10.3.3 allows remote attackers to affect confidentiality and integrity, related to IIS. |
| CVE-2010-2374 | Low | 2010-07-13 | Not applicable | No public exploit | Unspecified vulnerability in Solaris Studio 12 update 1 allows local users to affect confidentiality and integrity via unknown vectors. |
| CVE-2010-2373 | Medium | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the Console component in Oracle Enterprise Manager Grid Control 10.1.0.6 and 10.2.0.5 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2010-2372 | Medium | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Transportation Management component in Oracle Supply Chain Products Suite 6.1.1 allows remote attackers to affect integrity via unknown vectors, a different vulnerability than CVE-2010-2371. |
| CVE-2010-2371 | Low | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Transportation Management component in Oracle Supply Chain Products Suite 6.1.1 allows local users to affect confidentiality via unknown vectors, a different vulnerability than CVE-2010-2372. |
| CVE-2010-2370 | Medium | 2010-07-13 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Oracle Business Process Management component in Oracle Fusion Middleware 5.7 MP3, 6.0 MP5, and 10.3 MP2 allows remote attackers to affect integrity, related to BPM. |
| CVE-2010-0916 | Medium | 2010-07-13 | Not applicable | Working exploit published | Unspecified vulnerability in Oracle OpenSolaris 10 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to rdist. |
| CVE-2010-0915 | Medium | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Advanced Product Catalog component in Oracle E-Business Suite 11.5.10.2, 12.0.6, and 12.1.2 allows remote authenticated users to affect confidentiality and integrity via unknown vectors. |
| CVE-2010-0914 | Medium | 2010-07-13 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Convergence 1.0 allows remote attackers to affect confidentiality via unknown vectors related to Mail, Calendar, Address Book, and Instant Messaging. |
| CVE-2010-0913 | Medium | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Manager component in Oracle E-Business Suite 11.5.10.2, 12.0.6, and 12.1.2 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2010-0912 | Medium | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Framework component in Oracle E-Business Suite 11.5.10.2, 12.0.6, and 12.1.2 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2010-0911 | High | 2010-07-13 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Listener component in Oracle Database Server 9.2.0.8, 9.2.0.8DV, 10.1.0.5, 10.2.0.4, 11.1.0.7, and 11.2.0.1 allows remote attackers to affect availability via unknown vectors. |
| CVE-2010-0910 | Medium | 2010-07-13 | Not applicable | No public exploit | Unspecified vulnerability in the Data Server component in Oracle TimesTen In-Memory Database 7.0.6.0 and 11.2.1.4.1 allows remote attackers to affect availability via unknown vectors. |
| CVE-2010-0909 | Low | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Framework component in Oracle E-Business Suite 11.5.10.2, 12.0.6, and 12.1.2 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2010-0908 | High | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Framework component in Oracle E-Business Suite 12.1.2 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2010-0907 | High | 2010-07-13 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Secure Backup 10.3.0.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2010-0898, CVE-2010-0899, CVE-2010-0904, and CVE-2010-0906. |
| CVE-2010-0906 | High | 2010-07-13 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Secure Backup 10.3.0.1 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2010-0905 | Medium | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Manager component in Oracle E-Business Suite 11.5.10.2 and 12.0.4 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2010-0904 | Medium | 2010-07-13 | Not applicable | Working exploit published | Unspecified vulnerability in Oracle Secure Backup 10.3.0.1 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2010-0903 | High | 2010-07-13 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Net Foundation Layer component in Oracle Database Server 9.2.0.8, 10.1.0.5, 10.2.0.4, 11.1.0.7, and 11.2.0.1, when running on Windows, allows remote attackers to affect availability via unknown vectors. |
| CVE-2010-0902 | Medium | 2010-07-13 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Oracle OLAP component in Oracle Database Server 9.2.0.8, 9.2.0.8DV, 10.1.0.5, 10.2.0.4, 11.1.0.7, and 11.2.0.1 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2010-0901 | Low | 2010-07-13 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Export component in Oracle Database Server 9.2.0.8, 9.2.0.8DV, 10.1.0.5, 10.2.0.4, 11.1.0.7, and 11.2.0.1 allows remote authenticated users to affect confidentiality via unknown vectors related to Select Any Dictionary. |
| CVE-2010-0900 | Low | 2010-07-13 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Network Layer component in Oracle Database Server 9.2.0.8, 10.1.0.5, 10.2.0.4, 11.1.0.7, and 11.2.0.1, when running on Windows, allows remote attackers to affect availability via unknown vectors. |
| CVE-2010-0899 | High | 2010-07-13 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Secure Backup 10.3.0.1 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2010-0898, CVE-2010-0907, and CVE-2010-0906. |
| CVE-2010-0898 | High | 2010-07-13 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Secure Backup 10.3.0.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2010-0892 | Medium | 2010-07-13 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Application Express component in Oracle Database Server 3.2.0.00.27 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2010-0873 | High | 2010-07-13 | Not applicable | No public exploit | Unspecified vulnerability in the Data Server component in Oracle TimesTen In-Memory Database 7.0.6.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2010-0836 | Low | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Knowledge Management component in Oracle E-Business Suite 11.5.10.2, 12.0.6, and 12.1.2 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2010-0835 | Medium | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the Wireless component in Oracle Fusion Middleware 10.1.2.3 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2010-0083 | High | 2010-07-13 | Not applicable | No public exploit | Unspecified vulnerability in Oracle OpenSolaris 8, 9, and 10 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2010-0081 | Low | 2010-07-13 | No exploit published | No public exploit | Unspecified vulnerability in the Application Server Control component in Oracle Fusion Middleware 10.1.2.3 and 10.1.4.0.1 allows remote authenticated users to affect integrity via unknown vectors, a different vulnerability than CVE-2010-2381. |
| CVE-2009-3764 | Medium | 2010-07-13 | Not applicable | No public exploit | Unspecified vulnerability in the OpenSSO component in Oracle OpenSSO Enterprise 8.0 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2009-3763 | Medium | 2010-07-13 | Not applicable | No public exploit | Unspecified vulnerability in the Access Manager / OpenSSO component in Oracle OpenSSO Enterprise 7.1, 7, 2005Q4, and 8.0 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2009-3762 | Medium | 2010-07-13 | Not applicable | No public exploit | Unspecified vulnerability in Oracle OpenSSO Enterprise 8.0 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2010-0849 | High | 2010-04-01 | No exploit published | No public exploit | Unspecified vulnerability in the Java 2D component in Oracle Java SE and Java for Business 6 Update 18, 5.0 Update 23, 1.4.2_25, and 1.3.1_27 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. NOTE: the previous information was obtained from the March 2010 CPU. Oracle has not commented on claims from a reliable researcher that this is a heap-based buffer overflow in a decoding routine used by the JPEGImageDecoderImpl interface, which allows code execution via a crafted JPEG image. |
| CVE-2009-3555 | Critical | 2009-11-09 | Mitigation candidate | Exploited | The TLS protocol, and the SSL protocol 3.0 and possibly earlier, as used in Microsoft Internet Information Services (IIS) 7.0, mod_ssl in the Apache HTTP Server 2.2.14 and earlier, OpenSSL before 0.9.8l, GnuTLS 2.8.5 and earlier, Mozilla Network Security Services (NSS) 3.12.4 and earlier, multiple Cisco products, and other products, does not properly associate renegotiation handshakes with an existing connection, which allows man-in-the-middle attackers to insert data into HTTPS sessions, and possibly other types of sessions protected by TLS or SSL, by sending an unauthenticated request that is processed retroactively by a server in a post-renegotiation context, related to a "plaintext injection" attack, aka the "Project Mogul" issue. |
| CVE-2009-0217 | Medium | 2009-07-14 | No exploit published | No public exploit | The design of the W3C XML Signature Syntax and Processing (XMLDsig) recommendation, as implemented in products including (1) the Oracle Security Developer Tools component in Oracle Application Server 10.1.2.3, 10.1.3.4, and 10.1.4.3IM; (2) the WebLogic Server component in BEA Product Suite 10.3, 10.0 MP1, 9.2 MP3, 9.1, 9.0, and 8.1 SP6; (3) Mono before 2.4.2.2; (4) XML Security Library before 1.2.12; (5) IBM WebSphere Application Server Versions 6.0 through 6.0.2.33, 6.1 through 6.1.0.23, and 7.0 through 7.0.0.1; (6) Sun JDK and JRE Update 14 and earlier; (7) Microsoft .NET Framework 3.0 through 3.0 SP2, 3.5, and 4.0; and other products uses a parameter that defines an HMAC truncation length (HMACOutputLength) but does not require a minimum for this length, which allows attackers to spoof HMAC-based signatures and bypass authentication by specifying a truncation length with a small number of bits. |